Shadow IT refers to devices, applications, and services used within an organization without the knowledge, approval, or management of the IT team. Shadow IT assets can include personal devices, unauthorized software, rogue access points, unmanaged switches, and unapproved cloud services.
These assets operate outside established security controls. They create visibility gaps and can form shadow networks that are difficult to monitor. Without complete visibility, organizations may struggle to enforce security policies. They may also have difficulty maintaining accurate asset inventories and identifying unauthorized or compromised devices.
As businesses become increasingly decentralized and cloud-driven, managing Shadow IT has become an important cybersecurity challenge. Effective Shadow IT security requires continuous asset discovery and monitoring. These capabilities help identify unmanaged assets, reduce exposure, support compliance, and strengthen cyber resilience.
Shadow IT Security Risks
Shadow IT assets can create significant cybersecurity risks because they expand an organization’s attack surface. Unmanaged devices, unauthorized applications, and rogue network equipment can operate outside centralized security controls. This makes these assets difficult to detect and secure.
Unknown or unmanaged assets can create security blind spots and lead to shadow networks. These gaps make it harder for IT teams to identify suspicious activity and respond quickly. As a result, organizations face increased risks of data breaches, malware infections, unauthorized access, and compliance violations.
How Shadow IT Creates Unauthorized Network Connections
Shadow IT assets can create unauthorized network connections. Devices or network equipment may connect to corporate infrastructure without proper approval, configuration, or monitoring. These connections can bypass established security controls. They can also create visibility gaps for IT and security teams.
Common examples include:
- Personal Devices: When an employee connects a personal router, external drive, or application to the network, it becomes unmanaged. These connections enable file sharing, unapproved software installation, or bypassing security controls. As a result, the risk of data leaks and cyber threats increases.
- Rogue Access Points: Setting up an unauthorized wireless access point, whether for convenience or malicious intent, creates a shadow network connection. This weakens network security, making it easier for attackers to intercept traffic or gain unauthorized access to sensitive systems.
- Compromised Devices: If a network-connected device (such as a printer, IoT device, or server) is infected with malware, it can establish unauthorized connections to external servers. These compromised devices operate outside IT’s visibility, allowing cybercriminals to steal data or launch attacks from within the network.
Security Risks of Unauthorized Connections
Shadow IT assets introduce several critical security risks once they connect to the network without proper controls. IT security teams implement strict network configurations and protocols to protect the organization. However, when shadow IT assets bypass these protections, they introduce serious cybersecurity threats, including:
- Security Vulnerabilities: Unauthorized connections often lack firewalls, encryption, or endpoint protection, creating weaknesses that attackers can target.
- Spreading Malware: Shadow IT devices may already be compromised, allowing malware to spread across the network and infect critical systems.
- Data Breaches: Without the right access controls and monitoring, sensitive data can be exposed or stolen, causing compliance violations and financial losses.
These risks grow in regulated industries such as finance, healthcare, and government. Shadow IT can cause serious privacy and data handling violations.
How to Mitigate Shadow IT Asset Risks
To reduce shadow IT risks, organizations must improve network visibility and educate employees about the dangers of unauthorized devices. They should also enforce strict security policies.
This includes conducting regular audits and implementing device control solutions. Organizations should also encourage transparency and communication between employees and IT teams.
Sepio platform helps organizations gain full network visibility and detect unauthorized connections, reducing the risks posed by shadow IT assets. By securing all network-connected devices, IT teams can minimize the attack surface and protect against potential cyber threats.
Common Shadow IT Scenarios Handled by Sepio
To effectively address these risks, organizations need continuous visibility and control over all connected assets. Sepio helps IT teams detect and mitigate shadow IT through hardware-based visibility, continuous monitoring, and automated reporting. Key scenarios include:
- Rogue Wireless Access Points: Detection of unsupervised or unauthorized access points not managed by the corporate Wireless LAN Controller, preventing unapproved network extensions.
- Unauthorized Wireless Configurations: Identification of random MAC addresses, operational devices on guest Wi-Fi, and BYOD devices on production networks, ensuring proper segmentation and policy compliance.
- Non-Compliant or Risky Devices: Flagging devices with poor reputations, dual-use assets, or personal devices in unauthorized locations, helping enforce corporate device policies.
- Wired Network Misconfigurations: Discovery of unmanaged or unsupervised switches, multiple devices on the same port, or assets operating in incorrect VLANs, reducing exposure of sensitive network segments.
Through advanced filtering, tagging, and scheduled reporting, Sepio supports proactive monitoring and early detection of Shadow IT activity. These capabilities help organizations respond quickly while maintaining visibility, control, and compliance across their environments.
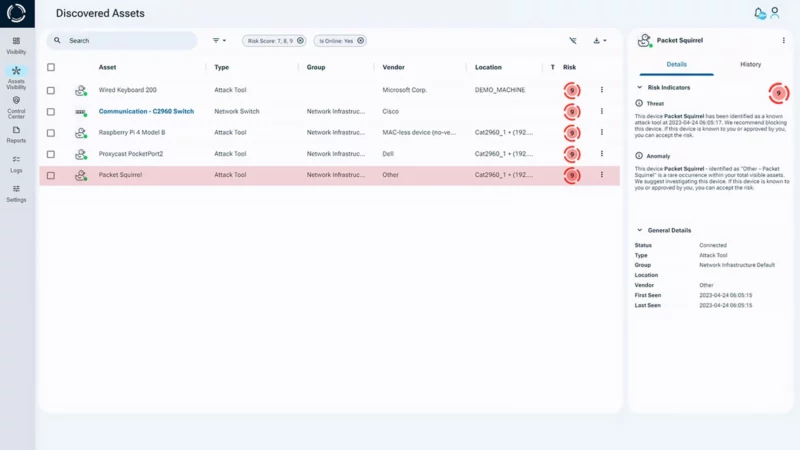
To support these capabilities, Sepio combines endpoint-level enforcement with deep network visibility.
At the endpoint level, the Sepio Agent provides lightweight, hardware-based protection with minimal system impact. It enables granular control over USB and peripheral usage, allowing only approved devices while blocking unauthorized ones. This prevents the use of rogue removable media, one of the most common vectors for malware and data exfiltration, without disrupting user productivity.
Hardware-Level Visibility and Continuous Asset Intelligence
At the network level, the Sepio Scan Engine continuously identifies and profiles connected hardware. It interacts directly with network infrastructure using secure protocols. Designed for scalability, it delivers detailed asset intelligence across complex environments. Frequent scanning also helps maintain up-to-date asset inventories.
Unlike traditional discovery tools that rely on software-based identification, Sepio uses hardware fingerprinting to identify devices by their physical characteristics. This approach helps detect spoofed, hidden, or disguised assets.
Sepio combines continuous monitoring with hardware-level visibility and control. This helps organizations detect and manage Shadow IT assets before they become serious security risks.
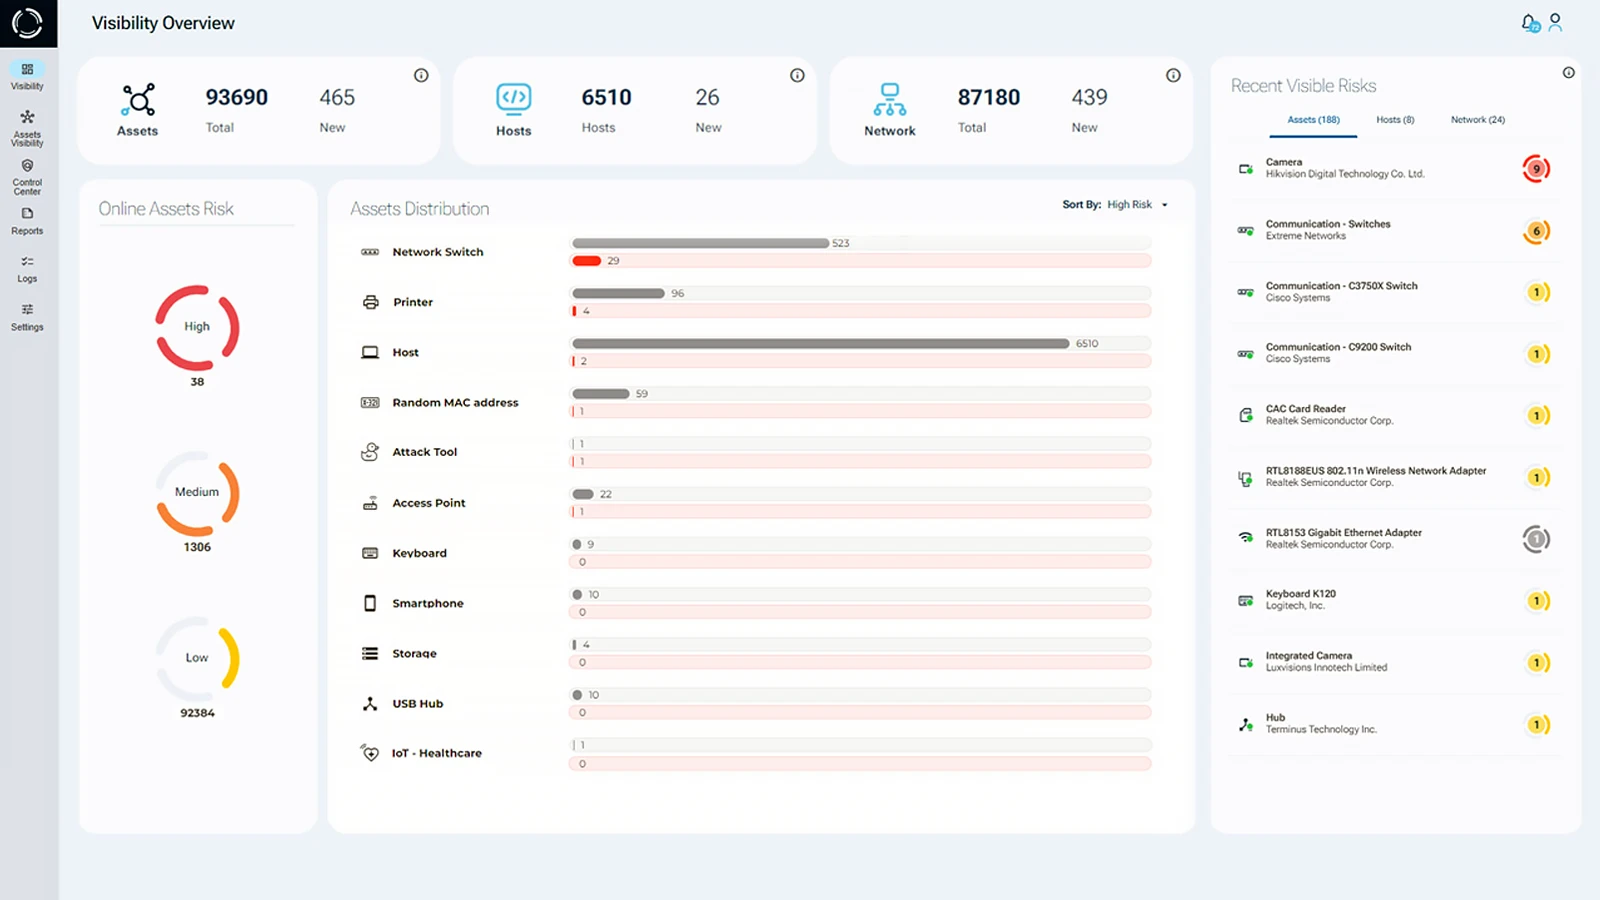
Manage Your Network Devices Effectively
Gaining full visibility into network devices is crucial for eliminating blind spots caused by shadow IT assets. By using physical layer data, organizations can detect and mitigate unauthorized devices that traditional security solutions overlook.
With Sepio, IT teams are empowered to make informed decisions, reduce risk exposure, and strengthen their overall cybersecurity posture.
Shadow IT is not just a security problem; it is also a business challenge. Understanding and addressing shadow IT enables organizations to maintain trust, meet compliance standards, and ensure smooth operations.
Schedule a demo to see how Sepio identifies hidden shadow IT assets, enforces policy, and helps secure your network in real time.
Talk to an expertFrequently Asked Questions
Shadow IT assets are devices, software, cloud services, and other technology resources used without the knowledge or approval of the IT department. Examples include unmanaged IoT devices, personal laptops, unauthorized applications, and rogue network equipment.
In cybersecurity, Shadow IT refers to technology operating outside established governance and security controls. Because these assets are often unknown to security teams, they create visibility gaps and increase organizational risk.
Shadow IT can introduce unauthorized access paths, expand the attack surface, create compliance challenges, and expose organizations to vulnerabilities that may go unpatched or undetected.
A shadow network is formed when unauthorized devices or infrastructure connect to an organization’s environment without IT oversight. Rogue access points, unmanaged switches, and personal networking equipment are common examples.
Organizations can identify Shadow IT assets through continuous asset discovery, device visibility, network monitoring, and hardware identity verification. These capabilities help security teams detect unmanaged or unauthorized devices across enterprise environments.