Ransomware is typically associated with compromised credentials, malicious software, phishing, and exploited vulnerabilities. But attackers can also take advantage of the hardware layer, using rogue, unauthorized, or manipulated devices to create an entry point into the environment.
Traditional cybersecurity controls such as firewalls, endpoint protection, Network Access Control (NAC), and intrusion detection primarily focus on software, identities, network traffic, and known device attributes. This can leave a critical blind spot at the physical layer, where a connected device may not always be what it claims to be. Hardware Attacks: The Art of Disguise describes how malicious hardware can disguise itself as legitimate equipment and potentially evade conventional security controls.
The Hardware Blind Spot
You cannot protect what you cannot accurately identify.
Unmanaged devices, unauthorized network equipment, rogue peripherals, dormant assets, and hardware impersonating trusted devices can exist outside traditional inventory and security controls. Sepio’s recent Zero Trust Hardware Access messaging emphasizes that identifiers such as MAC addresses, IP addresses, certificates, or asset records can provide useful information, but they do not independently establish what a device physically is.
This visibility gap can create opportunities for hardware-based ransomware attacks. A rogue or manipulated device may provide attackers with another path to establish access, circumvent existing controls, or introduce malicious activity into the environment. Sepio’s existing ransomware material specifically identifies unmanaged and rogue devices as potential entry points capable of bypassing traditional defenses.
From Hardware Visibility to Verified Device Truth
Effective hardware security requires more than maintaining an inventory of connected devices. Organizations need to understand what is connected, what each device really is, whether it belongs in the environment, what risk it represents, and what action should be taken. This reflects Sepio’s current Zero Trust Hardware Access framework.
Sepio provides this intelligence by analyzing physical-layer characteristics and creating a unique Hardware AssetDNA™ for connected assets. Rather than relying exclusively on identifiers reported by the device itself, AssetDNA helps establish hardware identity using physical-layer evidence and can surface anomalies associated with spoofing, impersonation, unexpected connections, and other hardware risks.
AI-Powered Hardware Superintelligence
Sepio combines physical-layer device intelligence, Hardware AssetDNA, advanced AI, and machine learning to transform hardware data into actionable security intelligence.
This Hardware Superintelligence enables organizations to move beyond simply knowing that a device exists. It helps security teams continuously discover assets, verify hardware identity, identify anomalies, understand device risk, and support informed Zero Trust decisions. Zero-Trust-Hardware-Access describes this progression as a move from hardware visibility toward continuous understanding and verification.
The approach can help organizations:
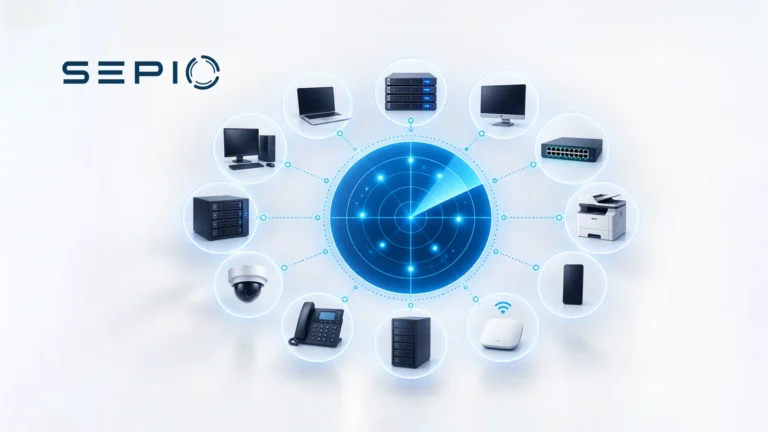
- Discover connected hardware including managed, unmanaged, dormant, hidden, and non-traditional assets.
- Verify device identity using physical-layer characteristics and Hardware AssetDNA instead of relying solely on self-reported attributes.
- Identify hardware anomalies and risk associated with unexpected devices, spoofing, impersonation, or unauthorized equipment.
- Apply policy-driven controls to support containment, blocking, isolation, escalation, or remediation through supported security controls and integrations.
Strengthening Ransomware Defense at the Hardware Layer
Ransomware defense should not stop at users, applications, endpoints, and network traffic. The physical devices accessing the environment also need to be continuously discovered, identified, and evaluated.
By extending Zero Trust principles to the hardware layer, organizations can reduce visibility blind spots, identify unauthorized or unexpected devices, and make more informed security decisions based on verified hardware intelligence.
Discover how hardware assets can become ransomware attack vectors and why protecting the physical layer is an essential part of a modern cybersecurity strategy.