Rogue devices on a network are unauthorized, unmanaged, hidden, or spoofed hardware connected to a network without the organization’s knowledge or approval. These devices can create security blind spots, bypass existing controls, and introduce significant cyber risks.
Rogue devices may include unauthorized laptops, rogue access points, IP KVMs, mouse jigglers, USB-based implants, IoT devices, and hardware designed to impersonate legitimate assets. Because many of these devices operate below the visibility of traditional IT and security tools, they can remain undetected while providing attackers with access to sensitive systems, networks, and data.
Continuous hardware asset visibility is essential for identifying rogue devices on a network, detecting hardware-based threats, and maintaining control over the attack surface.
Why Is Rogue Device Detection Critical
Every unidentified device represents a potential gap in an organization’s cybersecurity posture. Whether introduced intentionally or accidentally, unknown hardware can expand the attack surface, create compliance concerns, and complicate incident response efforts.
Traditional security tools are often designed to monitor users, software, and network traffic rather than validate the identity of connected hardware. As a result, rogue devices on a network, including unauthorized devices, spoofed equipment, and undocumented infrastructure, can remain connected for extended periods without being detected.
Continuous rogue device detection helps organizations establish trust in their asset inventory, improve security operations, strengthen Zero Trust initiatives, and reduce the likelihood of hardware-based threats impacting business operations. By identifying rogue devices on a network as they appear, organizations gain the visibility needed to investigate anomalies, enforce policies, and respond more effectively to emerging risks.
Rogue Device Detection Case Study
A Tier 1 bank audit revealed some irregularities. It became evident that invisible network devices, rogue devices, had continuous access to the internal and secured parts of the network. After investigating the bank’s computing assets, including the servers, desktop workstations, and management’s laptop, the team found no evidence of malware with remote access capabilities.
Subsequently, investigations focused on deep monitoring of incoming and outgoing communications from the network hoping there would be an indication as to what was occurring. Again, the investigators found no evidence of full remote access. The bank sought assistance from the cybersecurity investigations practice of a leading global consulting firm. The team discovered that the perpetrators had cloned an authentic laptop, spoofed laptop, belonging to the bank. It was connecting to the network infrastructure via an out-of-band channel in parallel to the existing and legitimate laptop, similar to hidden remote access devices such as IP KVMs, which can bypass traditional security controls.
The network access profile, certificate, and other authentication measures were authentic and valid, meaning none of the existing security and monitoring tools could detect the system as a rogue device on the network. The attackers had deployed a “ghost” device that remained undetected. Upon further investigation, the team discovered a small, unidentified hardware device installed in one of the distribution cabinets. This device provided remote access to the attackers, completely bypassing existing security measures.
Rogue Device Attack Study
With the growing sophistication of cyber threats, the concept of detecting rogue devices on network has become a crucial focus in ensuring network security. As new technologies emerge, attackers continue to innovate, using tools that are harder to identify.
In this case, the attackers used a legitimate off-the-shelf network router sold by a third party. In addition to its standard functionality, the device supported a virtual cable mode that allowed two devices installed in different locations to operate as though they were connected by a passive LAN cable. This capability enabled the attackers to reroute and tunnel communications through a simple switchboard application, intercept traffic, inject data packets, and stream communications back into the network. It also facilitated more advanced man-in-the-middle (MiTM) attacks.
These rogue devices on the network were particularly difficult to detect because they operated without an IP or MAC address. As a result, traditional Intrusion Detection Systems (IDS), Network Access Control (NACs) solutions, and network monitoring tools were unable to identify them. The manipulation occurred at the Physical Layer and the Data-Link Layer (Layer 2), where higher-layer communications appeared legitimate and secure, making detection significantly more challenging.
How Rogue Devices Bypass Authentication Methods
In this specific incident, the perpetrators utilized a BeagleBone board running USBProxy. When connected between the scanning device and the system storing legitimate fingerprint records, it enabled the attackers to bypass the authentication process.
The BeagleBone requires no additional hardware and provides a rich set of input/output capabilities, making it easy to interface with external electronics and emulate trusted devices.
This case highlights a key weakness in traditional security approaches: rogue devices on a network can bypass conventional authentication mechanisms while appearing legitimate to existing security controls. The use of specialized hardware such as the BeagleBone demonstrates the importance of continuous monitoring and hardware-based asset visibility. Organizations need the ability to identify device identities based on their physical characteristics rather than relying solely on software attributes, network behavior, or authentication status.
Rogue Device Detection Software
Sepio is a leader in rogue device detection software, helping organizations discover, identify, and mitigate unauthorized, hidden, and spoofed devices across their environment. By providing continuous visibility and hardware trust, Sepio enables organizations to establish the identity of connected assets, assess risk, and enforce security policies throughout the asset lifecycle.
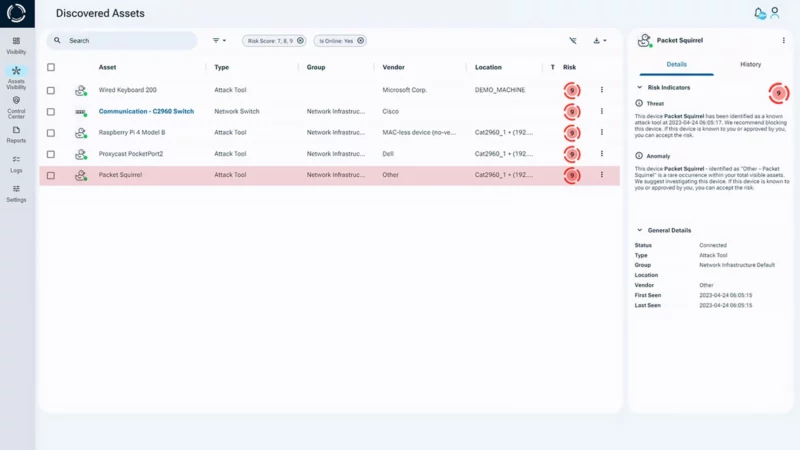
Sepio’s AssetDNA™ technology, rooted in the physical layer, identifies assets based on their hardware characteristics rather than their behavior. This approach enables the discovery and identification of managed, unmanaged, hidden, invisible, and spoofed devices that may be missed by traditional security tools. Through physical-layer intelligence, Sepio uncovers the true source of asset risk without relying solely on network behavior or device declarations.
Sepio provides hardware asset intelligence designed to help organizations:
- Discover connected assets.
- Establish hardware identity.
- Compare observed characteristics with expected profiles.
- Assess asset risk.
- Apply appropriate policies.
- Continuously verify assets throughout their lifecycle.
As a rogue device detection tool, Sepio helps organizations identify unauthorized devices, investigate anomalies, validate trusted assets, and prioritize remediation efforts. Security and IT teams gain actionable insight into the hardware operating across their environments, enabling a stronger foundation for asset security, governance, and risk management.
Having visibility into connected hardware is essential, but visibility alone is not enough. Organizations must be able to identify, verify, assess, and control the devices operating across their environments. By combining hardware asset intelligence, continuous identity verification, and risk-based policy enforcement, Sepio helps organizations strengthen their hardware security posture and reduce exposure to hardware-based threats.
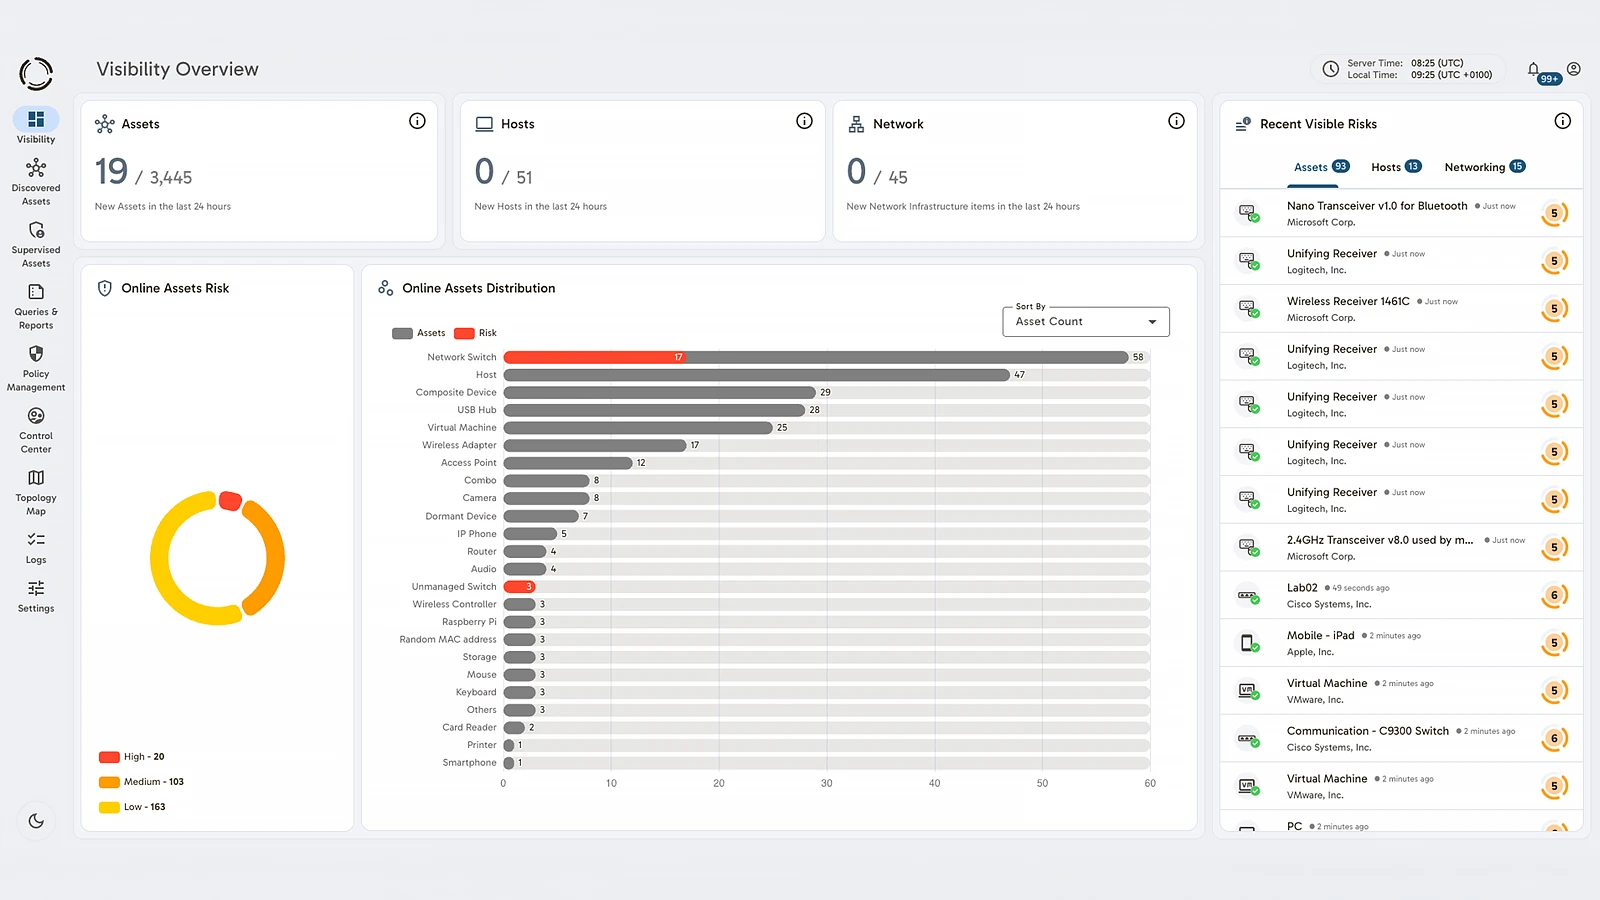
Sepio’s Asset Risk Management
Sepio provides real-time visibility into the hardware operating across enterprise environments, helping organizations identify unknown assets, assess risk, and strengthen their hardware security posture. By leveraging AssetDNA™ technology and policy-driven controls, Sepio establishes hardware trust, highlights assets that require attention, and enables teams to focus on the risks that matter most.
Security and IT teams gain continuous insight into managed, unmanaged, hidden, and spoofed devices, helping them accelerate investigations, identify compliance gaps, validate trusted assets, and prioritize remediation efforts. This intelligence enables organizations to better understand their hardware attack surface and make informed risk-management decisions.
See every known and unknown device. Prioritize and mitigate risks.
Schedule a demo to learn how Sepio’s patented technology helps organizations establish hardware trust, gain visibility into connected assets, and take control of hardware-related risks.
Frequently Asked Questions
A rogue device on a network is any hardware asset connected to a network without proper authorization, visibility, or oversight. Rogue devices on a network may include rogue access points, unauthorized laptops, IP KVM devices, USB-based implants, IoT devices, and hardware designed to impersonate legitimate assets.
Many security tools rely on information reported by the device itself, such as MAC addresses, hostnames, IP addresses, or software agents. Rogue devices on a network can manipulate, spoof, or evade these methods, making accurate identification difficult and allowing unauthorized hardware to remain undetected.
Organizations identify rogue devices on a network by establishing the identity of connected hardware and continuously monitoring for unauthorized, hidden, spoofed, or unmanaged assets. Hardware-based identification methods can help detect devices that traditional security tools may overlook.
Sepio uses its patented AssetDNA™ technology to identify hardware assets based on physical-layer (Layer 1) characteristics. Rather than relying solely on device-reported information, AssetDNA™ establishes trusted hardware identities and helps organizations identify rogue devices on a network, including hidden, spoofed, unauthorized, and unmanaged assets.
Traditional discovery tools often depend on network traffic analysis, software agents, IP addresses, or MAC addresses. Sepio validates device identity at the physical layer, allowing security teams to identify assets based on what they actually are, not what they claim to be.
Yes. Because AssetDNA™ verifies hardware identity using Layer 1 characteristics, Sepio can help identify devices attempting to impersonate trusted hardware and uncover discrepancies that traditional asset discovery tools may miss.
Yes. Sepio provides visibility into connected hardware assets, including IP KVM devices. This helps organizations identify unauthorized, undocumented, or non-compliant remote management devices within their environment.