Hardware-Based Security
Hardware-based security uses physical components and built-in technologies to protect computers and networks from cyber threats. It provides greater visibility into connected devices and stronger mechanisms for verifying system integrity. These capabilities make it an important part of a comprehensive cybersecurity strategy.
As hardware attack tools become more accessible, particularly in government, healthcare, finance, energy, and transportation, hardware-based security becomes increasingly critical. These sectors provide essential services, making their cybersecurity and operational security matters of national importance.
Combining hardware security with a Zero Trust model strengthens overall cybersecurity and helps reduce risk. In this model, no user or device is trusted by default. Instead, every access request is evaluated based on factors such as identity, behavior, and context. This approach helps ensure that only verified users and trusted hardware can access sensitive data.
Hardware Based Attacks and Rogue Devices
Hardware-based attacks use rogue devices that operate at the physical layer. This hardware can evade traditional network security tools by disguising itself as legitimate human interface equipment. For example, a spoofed keyboard may appear to be a normal peripheral to the system while actually performing malicious actions.
Some hidden devices on the network also operate at the physical layer. They bypass important security controls such as Network Access Control (NAC). Since they do not raise alerts, they are extremely dangerous. They can stay hidden for a long time.
For a hardware attack to work, the hacker first needs to physically reach the system. Once a rogue device, a hardware attack tool, is plugged into the network, it can let the hacker get in remotely. The hacker can then steal data, spy on users, inject malware, or launch other attacks like DDoS, MiTM or Evil Maid.
Critical infrastructure is often a target for these hardware based attacks. Even if the attack causes no damage, just gaining access can harm public trust and hurt national security. That’s why hackers are often linked to governments.
Hardware Based Security Risks
Each IT infrastructure has unique hardware based security risks, but many share the same weak spots:
Outdated Legacy Systems
Many critical infrastructure environments rely on legacy systems that are difficult or impossible to update. These systems were designed to address the threats of the past, not today’s evolving threat landscape, making them more vulnerable to attack.
When security patches or upgrades cannot be applied, vulnerabilities can remain unaddressed and create persistent security gaps. Hackers can exploit these weaknesses to gain access to systems, increasing the organization’s overall cybersecurity risk.
Integrated Technology Environments
Modern environments increasingly connect IT, OT, and IoT systems. While this integration improves efficiency and enables new capabilities, it also expands the attack surface and introduces new cybersecurity risks. A cyberattack can even have real-world physical consequences, as demonstrated by the Stuxnet attack.
Hackers may need only one vulnerable device or connection to bypass existing security controls and compromise an organization’s security posture. Publicly accessible IoT devices, for example, can provide hackers with physical proximity to connected systems, creating opportunities for hardware-based attacks. This makes visibility into connected hardware and the ability to verify its security status an increasingly important part of a modern cybersecurity strategy.
Challenges in Large Organizations
Large organizations often have thousands of connected network assets, creating significant challenges for visibility, security, and risk management. Identifying, monitoring, and securing every asset across a complex environment can be difficult. Without visibility into an asset, security teams cannot effectively assess its risk, enforce security policies, or protect it as part of the organization’s broader security strategy.
Also, these organizations may not have full visibility into the physical layer. Some hospital areas have weak physical security, making it easy for and evil patient to carry out hardware based attacks.
Worse, some departments might follow weaker security rules than others. If one team has poor controls, the whole network security is at risk. You’re only as strong as your weakest link.
Zero Trust Hardware Based Security
Many organizations still trust internal users and devices too much. This trust gives hackers an easy path if they gain access from the inside.
The Zero Trust removes the idea of trust, every user and device must be checked each time they try to access the network. It also uses micro segmentation to break the network into smaller zones. This limits how far an hacker can go if they get in.
Micro-segmentation is especially helpful in complex, connected systems like those in critical infrastructure.
Zero Trust is even stronger when paired with Zero Trust Hardware Access (ZTHA). This adds another layer of defense by focusing on physical devices.
Connected Assets Visibility
To properly implement a Zero Trust Architecture, organizations need full visibility into all connect network assets, especially when it comes to hardware based attacks. Hardware based security starts with knowing the true identity of every asset on the network. This helps block rogue tools that try to sneak past defenses. These unauthorized assets often hide or masquerade as legitimate systems, which makes them hard to detect. If the system doesn’t verify a device’s identity, a rogue device can still connect to the network.
Endpoint and Network Hardware Security
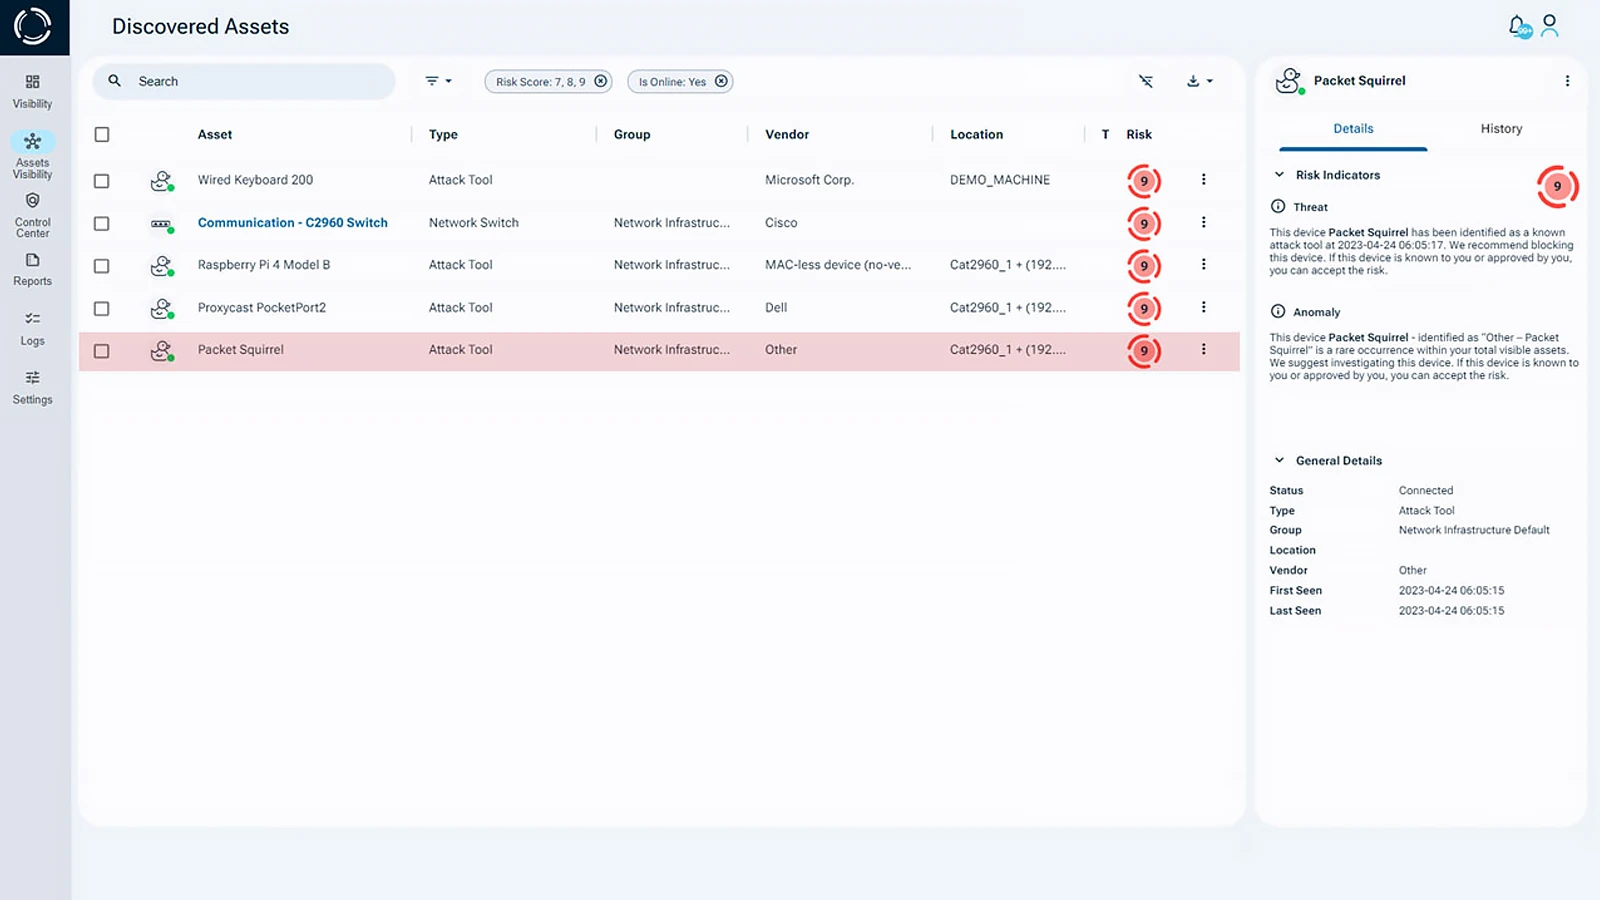
Sepio’s Asset DNA provides a full profile of every device, whether it’s IT, OT, IoT, even those without a unique ID.
Unlike tools that rely on behavior analysis, Sepio uses patented algorithms to avoid false positives. This gives you accurate, trusted visibility into your Cyber-Physical Systems (CPS), without being misled by fake device profiles.
With Sepio, your cybersecurity team gains clear, data-driven insights to identify and manage hardware risks and strengthen its overall security posture. This helps organizations build greater trust in their hardware environment and defend against hardware-based attacks.
Actionable Risk Prioritization
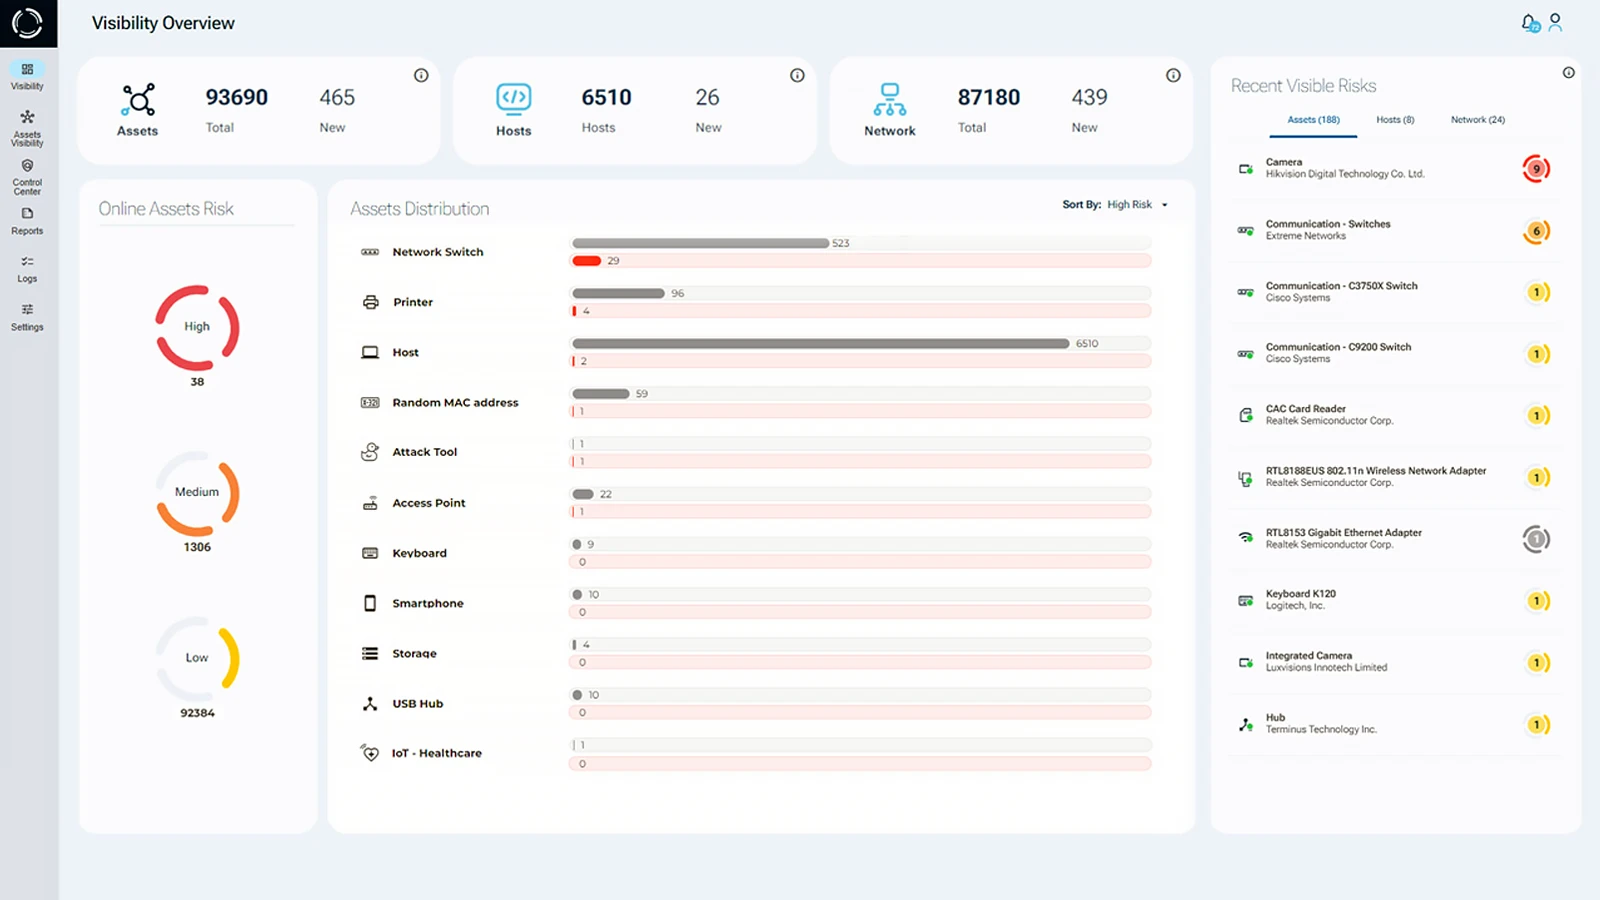
Sepio assigns a risk score to every connected asset. This score is based on Asset DNA, business context, location, and custom rules. Devices are grouped into high, medium, or low risk levels.
This helps your team spot threats faster, fix compliance issues, and prevent damage before it happens.
Sepio monitors assets in real time. If a device starts acting differently or becomes more risky, it immediately alerts your team. This way, you can respond faster and stay ahead of potential threats.
Key Benefits
- Full visibility of all IT, OT, IoT, and IoXT devices, without looking at network traffic
- Automatic detection and control of rogue USB and network hardware
- Strong protection against hardware based attacks, insider threats, and supply chain risks
See Every Known and Shadow Asset
Talk to an expert. It will help you understand how to use Sepio’s patented technology to gain control of your asset risks.
Talk to an expert