IoT is transforming how healthcare services are delivered, from remote patient monitoring to connected medical equipment in hospitals. Today, healthcare environments rely on a wide range of Internet of Things (IoT) assets, including wearables, imaging systems, infusion pumps, and smart monitoring tools. These connected technologies improve patient care, operational efficiency, and real-time decision-making.
However, as the number of connected medical devices grows, so does the attack surface. Many healthcare IoT assets operate with limited visibility and outdated security, creating potential entry points for cyber threats.
Understanding how IoT is used in healthcare, and where the risks lie, is essential for protecting both patient data and critical medical systems.
IoT Devices in Healthcare and Patients’ Care
Most developed countries have transitioned their healthcare systems from paper-based systems to a digital one. Digital healthcare applications and Internet of Medical Things (IoMT) devices are now internet connected and being used across all health sectors.
The use of IoT in healthcare devices brings numerous benefits for patients’ care. Internet-connected devices enable interoperability and machine-to-machine communication, facilitating a smoother flow of data and information exchange. This allows for the automation of patient care workflows, freeing up human efforts and capabilities for more effective use elsewhere. Furthermore, the capabilities of IoT in healthcare reduce human errors and eliminate many decision delays.
Internet of Medical Things (IoMT)
Internet of Medical Things devices can support real-time patient monitoring. It involves the use of wireless wearable health devices. These IoT devices can provide reminders for various health-related tasks. Encompassing calorie intake, sleep and exercise patterns, and vital signs tracking, including blood pressure and glucose monitoring (World Diabetes Day). They can also enhance the well-being of elderly patients by monitoring their health conditions. This is especially beneficial for those living alone. As any deviations or disruptions in their routines trigger alerts to both family members and healthcare providers.
Internet of Medical Things devices also play a vital role for both physicians and hospitals. In the case of physicians, wearables and home monitoring devices integrated with IoT enable efficient tracking of patients’ health data. Additionally, IoT facilitates telemedicine, offering clinical services to patients without requiring a face-to-face visit.
In hospitals, IoT in medical devices can be used to track the real-time location of medical equipment, including wheelchairs, defibrillators, nebulizers, and oxygen pumps. This real-time tracking enhances efficiency by providing immediate analysis of medical staff deployment across various locations. Furthermore, IoT devices can also play a crucial role in infection control through hygiene monitoring, mitigating the spread of infections among patients.
IoT Devices and Patient Data
Despite the benefits that IoT applications in healthcare bring to the sector, there are a plethora of healthcare cybersecurity challenges. Because healthcare providers perform critical and complex operations, they require access to highly sensitive data. This is particularly important when protecting personal health information (what is PHI?).
Personal digital health data is extremely attractive to attackers since it can sell for almost 300x the amount of personally identifiable information (PII). This makes the healthcare industry a primary target for hackers.
With greater numbers of IoT devices in use, the more digital entry points are available to attackers (IoT Security). This poses a threat not only in terms of accessing patient health data with compromised devices (rogue devices), but also in spreading throughout an organization’s network. Furthermore, the increased reliance on the supply chain is enhancing the security risks associated with IoT devices, as numerous suppliers are also adopting this technology. Consequently, there are more digital entry points that hackers can exploit. This heightens the importance of robust cybersecurity asset risk management in the healthcare sector.
Healthcare Networks Cybersecurity
Attackers can conduct a data breach, stealing patients’ data and selling it on the dark web. Alternatively, they may use the stolen data to create fake IDs for purchasing drugs and medical equipment, both of which they can then sell. This is the greatest concern for around 40% of healthcare providers. More malicious hackers may attempt to take control of IoT devices themselves, which could have fatal consequences if successful. This threat to patient safety is a major risk to the healthcare industry (watch: Ransomware in Healthcare – Evil Patient).
The use of IoT devices in the healthcare sector presents significant risks because healthcare cybersecurity is often viewed as a hindrance to operations (Hospital Cyber Resiliency Initiative). With patient care at the forefront of concerns, cybersecurity measures often slow down productivity. In an industry that regularly performs time-sensitive operations, every second is vital. As a result, cybersecurity investments are often deprioritized in favor of patient care initiatives. It is therefore understandable why employees have such a lack of awareness surrounding cyber risks and the various actions they can take to enhance security. Hence, the health industry is highly vulnerable when utilizing IoT devices (Human Factors in Cybersecurity).
Cybersecurity Measures for the Healthcare Industry
The healthcare industry needs to enhance its cyber security culture. Through education and training, staff should develop greater awareness of IoT device security risks (IoMT Security). However, reliance on staff is most definitely not sufficient (Insider Threat).
Other measures that should be implemented include enhanced authentication such as multi-factor and/or biometric sensors authentication to reduce the chances of a bad actor gaining access to sensitive data. Furthermore, the principle of least privilege will greatly benefit the security posture of the health industry. By only being able to access the necessary information required to conduct an activity, there will be fewer individuals who have access to highly sensitive data.
For the patient, it would be a good to limit the data being provided. When it comes to health this can be challenging. But consider whether the data that you are giving to your doctor is of utmost importance. When contemplating if you should engage in telemedicine services, ponder whether it really is such an inconvenience to visit your doctor face-to-face. If you can, then it might be better to do so.
Internet Connected Healthcare Devices
With the increasing use of IoT connected devices in healthcare networks, organizations are struggling to identify which devices are part of their infrastructure (Connected Healthcare Devices). From a cybersecurity point of view, this is extremely dangerous as it increases the chances of a successful IoT hardware attack. Again, these measures alone do not suffice, and cybersecurity software that can detect if an attack is occurring should support them.
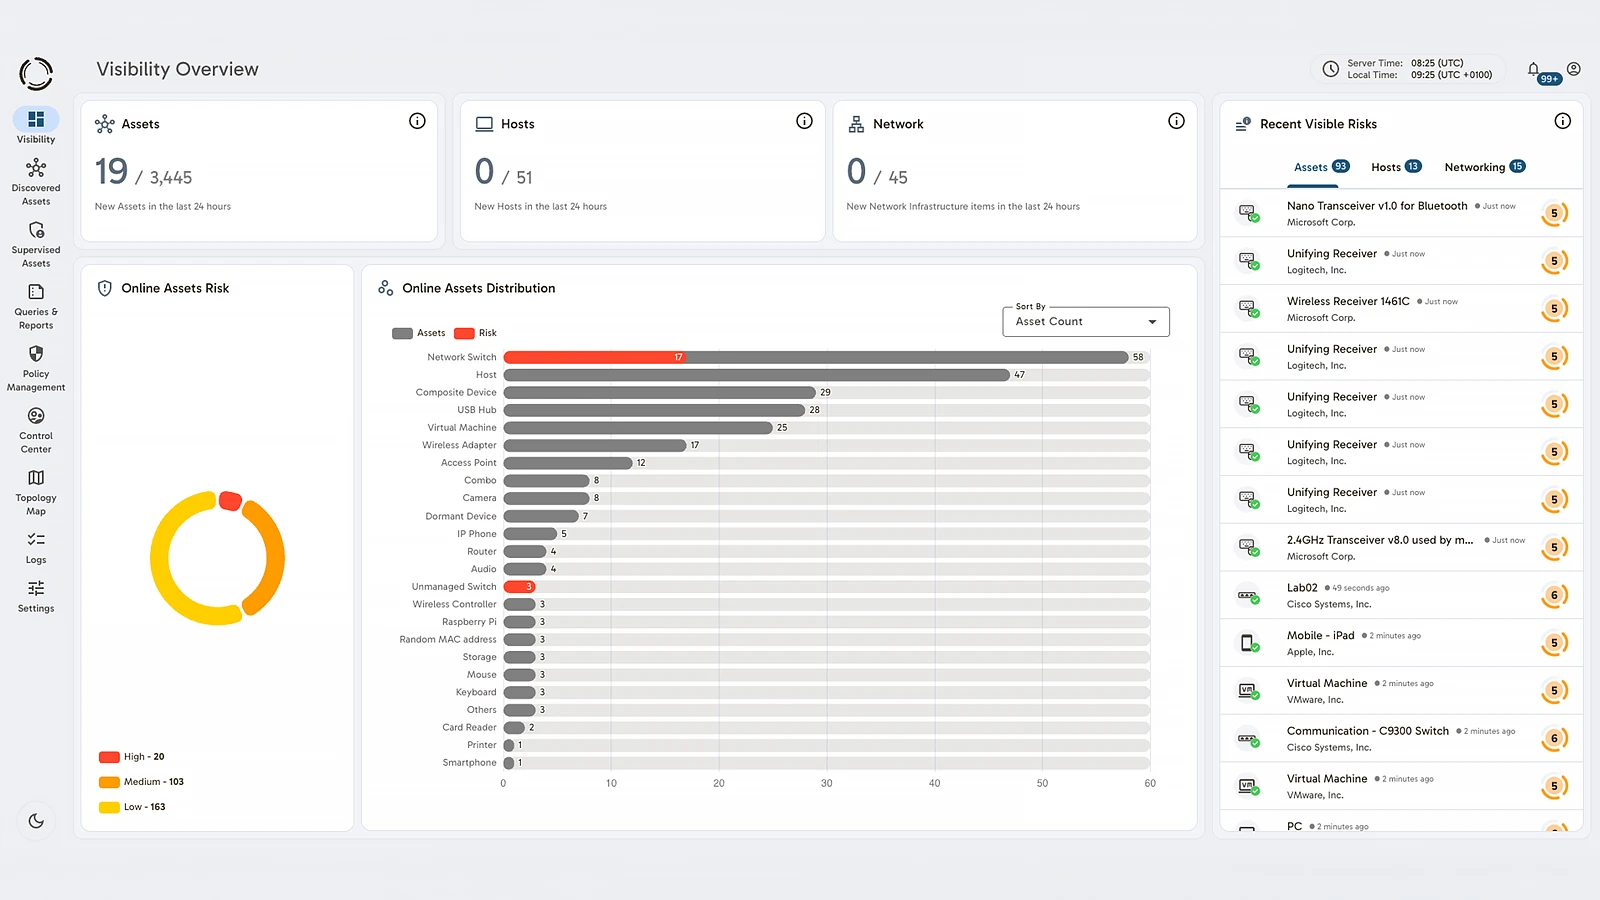
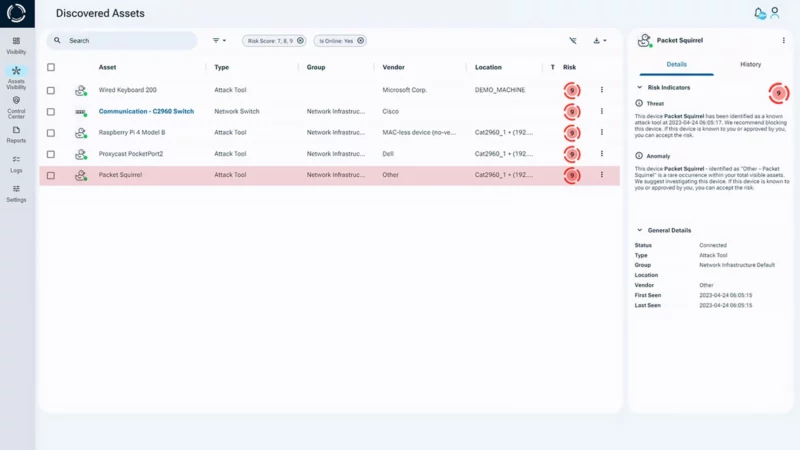
Sepio provides enterprises with full visibility to whatever is connected to the network infrastructure. Identifying hidden and malicious IoT devices operating over network and USB interfaces (Bad USB).
IoT Healthcare Security
As the only company in the world to verify physical layer data, Sepio identifies, detects, and manages all connected devices across network environments. No IoT device goes unmanaged. This total visibility enables us to achieve a stronger security posture. We no longer need to depend on manual reporting, legacy inventory reports, and employee compliance to determine if a malicious actor has installed a vulnerable IoT device.
Sepio now provides answers to questions such as:
- Do we have an IoT attack tool or spoofed device in our network?
- How many IoT devices do we have connected to our network?
- Who are the top 5 vendors for IoT devices found in our network (invisible network devices)?
- Where are the most vulnerable switches in our network (unmanaged switch)?
Having visibility across all IT digital assets provides the organization with a more comprehensive cybersecurity defense.
With so much of our data already online, attackers can easily determine where we like to hang out. Or what we like to eat, what music we like to listen to, and do damage with this data. Do we really need them to know what we aren’t advertising to our social media followers?
See every known and shadow asset. Prioritize and mitigate risks.
Talk to an expert. It will help you understand how to use Sepio’s patented technology to gain control of your asset risks.