Zero Trust Device Security extends the principles of Zero Trust to every device requesting access to enterprise resources. Based on “never trust, always verify,” it requires organizations to continuously validate not only user identity and authorization, but also whether the device requesting access can be trusted.
Traditional Zero Trust strategies typically focus on identities, applications, endpoints, and network policies. However, they can still depend on information that a device presents about itself. If that information is spoofed, manipulated, or incomplete, a rogue or unmanaged device may appear legitimate.
Sepio addresses this hardware trust gap through Zero Trust Hardware Access (ZTHA), powered by Hardware Superintelligence. By analyzing devices at the physical layer, Sepio helps organizations establish what a connected device actually is, assess its risk and trustworthiness, and make informed access and security decisions.
The result is a critical additional dimension of Zero Trust: verify what the physical device actually is, not just what it claims to be.
What is Zero Trust Architecture?
Zero Trust Architecture (ZTA) is a cybersecurity approach based on the principle of “never trust, always verify.” Instead of automatically trusting users or devices because they are inside a corporate network, Zero Trust requires authentication, authorization, and evaluation before access to resources is granted.
This approach has become increasingly important as enterprise environments have expanded beyond traditional network boundaries. Cloud services, remote work (WFH), BYOD, IoT, and interconnected devices mean that users and assets can access organizational resources from many locations and environments.
Traditional perimeter-based security assumed that entities inside the network were more trustworthy than those outside it. Today, compromised devices, insider threats, shadow IT, rogue hardware, and sophisticated attackers can operate on either side of that perimeter.
However, effective Zero Trust depends on reliable device identity. If you cannot verify the device, how can you trust the access decision?
Why Zero Trust Needs Device Trust
Device trust helps determine whether the device requesting access can be trusted to interact with a network, application, or resource. Authenticating the user alone is not enough. A legitimate user could connect through a compromised device, while a rogue or spoofed device could attempt to impersonate an authorized asset.
Zero Trust therefore needs to answer questions such as:
- What device is requesting access?
- Is the device what it claims to be?
- Is it managed, unmanaged, or unknown?
- What risk does it represent?
- Should it be allowed to access this resource?
Traditional security controls may rely on software, credentials, network identifiers, or other information reported by the device. This can create a hardware trust gap when that information is incomplete, manipulated, or spoofed.
Device trust cannot rely solely on what a device claims to be. Organizations need a reliable way to establish what the device actually is.
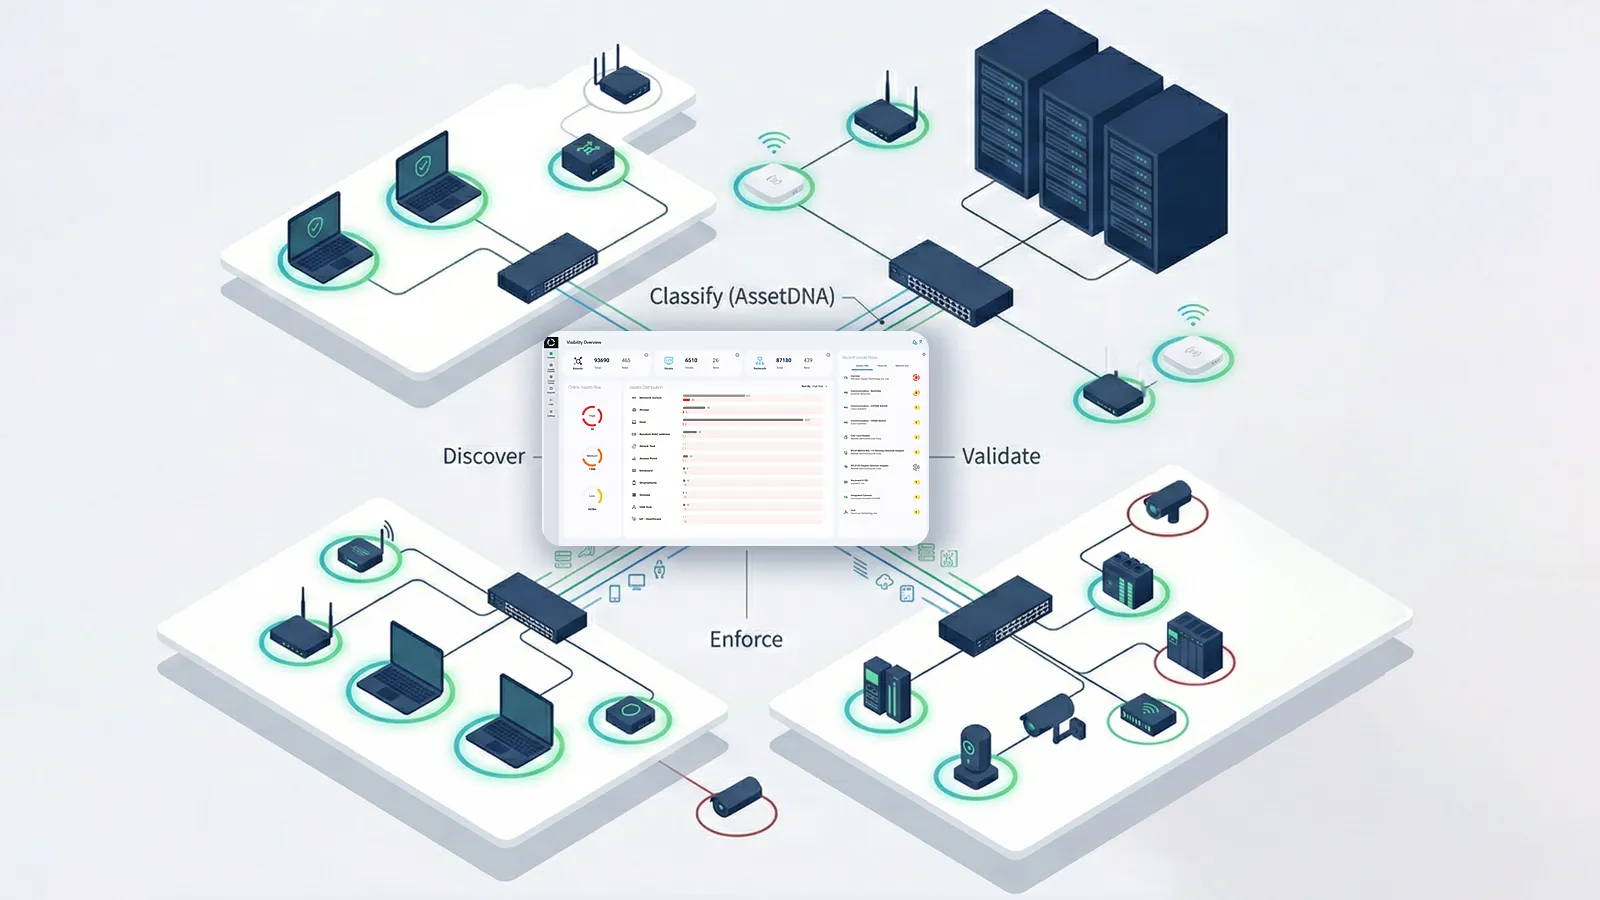
Verifying Device Integrity in Zero Trust
A Zero Trust solution that verifies device integrity should go beyond credentials, network location, and software-reported information. It should help establish what the physical device actually is, assess its trustworthiness and risk, and use that information to support access decisions.
Key capabilities should include:
- Accurate device identification: Establish the identity of the connected hardware.
- Continuous device verification: Continuously evaluate device trust rather than relying on a one-time authentication.
- Rogue and spoofed device detection: Identify hardware attempting to impersonate legitimate assets.
- Visibility into unmanaged devices: Discover devices outside conventional endpoint management.
- BYOD and IoT visibility: Identify connected devices that may not support traditional security agents.
- Device risk assessment: Determine the potential risk associated with a connected device.
- Policy enforcement: Use verified device intelligence to inform security and access decisions.
Together, these capabilities provide the foundation for applying Zero Trust principles to the hardware itself.
How to Achieve Zero Trust Device Security
Achieving Zero Trust Device Security requires continuous visibility into connected hardware, reliable device identification, and controls that respond to device trust and risk.
Sepio addresses these requirements through Zero Trust Hardware Access (ZTHA), powered by Hardware Superintelligence. This approach combines Physical Layer Visibility, Hardware Access Control, and Rogue Device Mitigation to help organizations identify, assess, and control the hardware accessing their environments.
Physical Layer Visibility
Zero Trust Architecture relies on accurately identifying both users and devices before granting access. However, hardware-based attacks often involve rogue devices that hide or spoof their identities. These hardware attack tools manipulate authentication and authorization processes, presenting themselves as legitimate assets.
As a result, Zero Trust controls may be bypassed, and access is granted based on false information. This undermines the effectiveness of Zero Trust security and enables attackers to infiltrate the network.
How Sepio Mitigates This Challenge
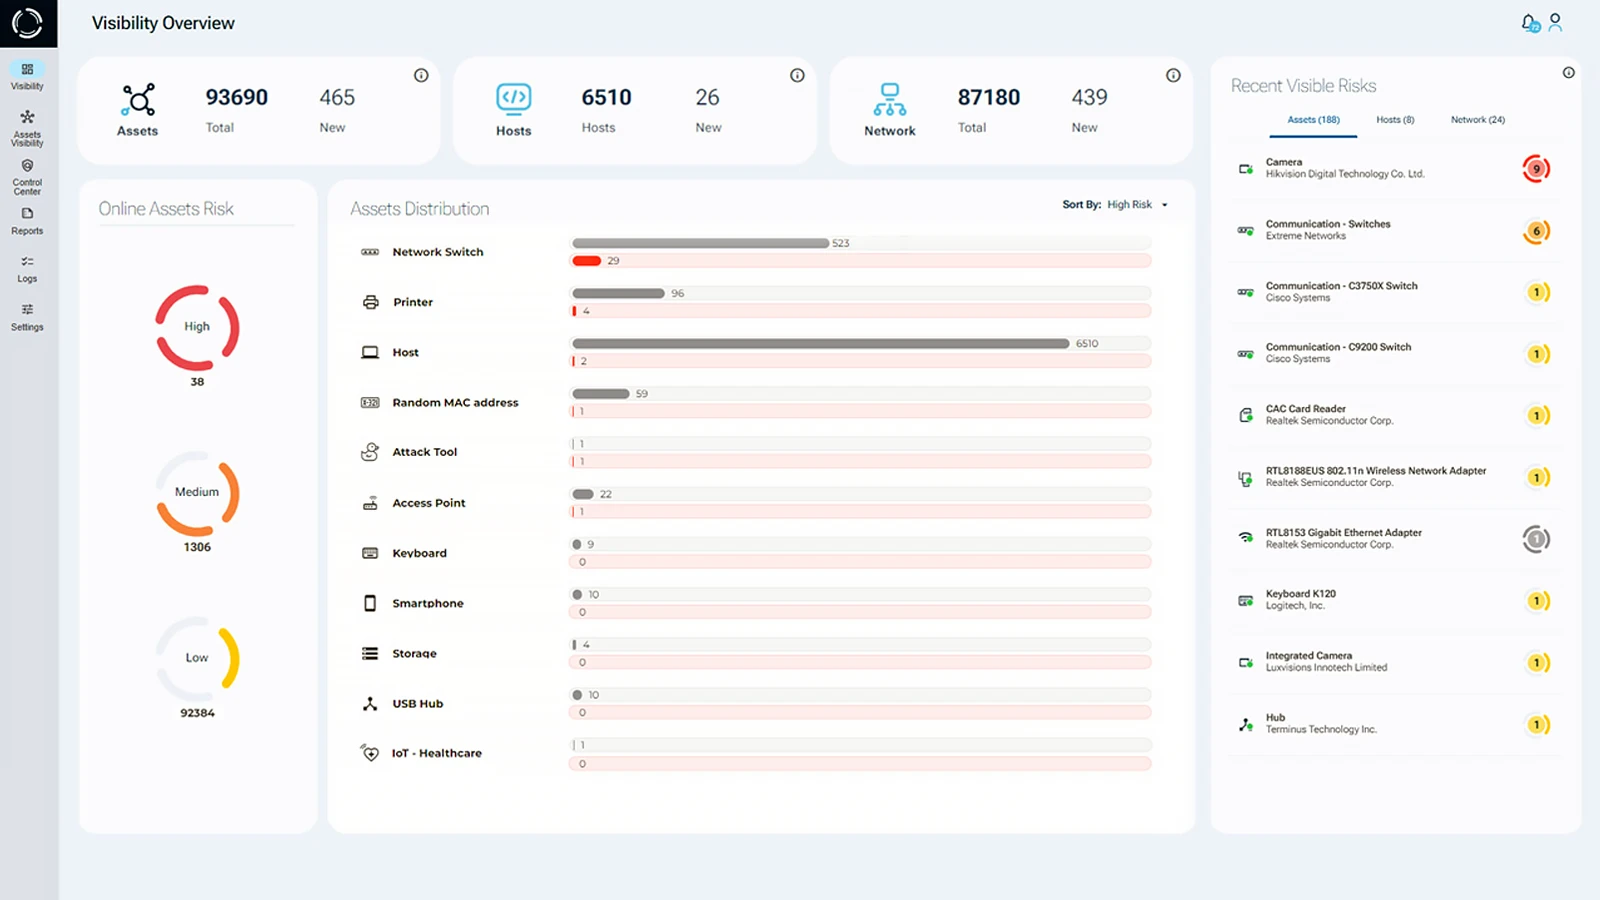
Sepio provides complete asset visibility through Physical Layer (Layer 1) fingerprinting. As the only solution offering full Layer 1 coverage, Sepio detects all assets operating within the enterprise environment, including managed, unmanaged, and hidden devices.
Using physical-layer electrical characteristics combined with machine learning, Sepio generates a unique digital fingerprint for every connected asset. These fingerprints are compared against an extensive threat intelligence database to:
- Reveal the true identity of devices
- Detect rogue and spoofed assets
- Identify vulnerable or malicious hardware in real time
- Ensure continuous visibility across the infrastructure
This enables organizations to validate every connected asset based on immutable physical attributes.
Policy Enforcement and Micro-Segmentation
Zero Trust relies on access policies to enable micro-segmentation and the principle of least privilege (PLP). These policies define which network segments and resources each entity may access.
However, when hardware attack tools impersonate legitimate assets or remain invisible to security systems, policies cannot be enforced effectively. Unauthorized devices may bypass segmentation controls and move laterally across the network.
Additionally, access policies are built on asset and traffic data. Incomplete visibility leads to inaccurate policies, weakening their reliability and effectiveness.
How Sepio Mitigates This Challenge
Sepio enforces Hardware-Based Access Control that governs network access using device-level physical characteristics rather than easily spoofed credentials.
Key capabilities include:
- Policy enforcement based on hardware fingerprints
- Granular and adaptive access controls
- Real-time alerts for vulnerable or high-risk devices
- Integration with threat intelligence
This ensures that micro-segmentation policies are applied to all devices, visible or hidden, using accurate, verified information. As a result, enterprises can implement reliable, risk-based access controls.
Rogue Device Mitigation
When visibility and access controls are compromised, organizations cannot confidently protect their critical assets. If a rogue device is mistakenly trusted, attackers can exploit access privileges to steal data, disrupt operations, or compromise systems.
This creates uncertainty around the integrity and security of enterprise resources.
How Sepio Mitigates This Challenge
Sepio’s Rogue Device Mitigation capability automatically initiates response actions when unauthorized or malicious hardware is detected.
Once a device violates predefined security policies, Sepio:
- Blocks the device immediately
- Prevents lateral movement
- Stops unauthorized access attempts
- Enforces Zero Trust controls at the hardware level
By neutralizing threats at the point of entry, Sepio prevents attackers from bypassing micro-segmentation and other security mechanisms. This proactive approach protects sensitive data and critical infrastructure from hardware-based attacks.
Benefits of Zero Trust Device Security
Implementing Zero Trust Device Security with physical-layer verification helps organizations:
- Elimination of network blind spots
- Prevention of spoofed or rogue device access
- Reliable micro-segmentation across all devices
- Reduced insider threat risk
- Continuous, real-time monitoring and proactive mitigation
Traditional Zero Trust controls focus on users, identities, and applications. Sepio extends Zero Trust Device Security to the hardware layer, helping organizations verify device identity, maintain visibility across connected assets, and make access decisions based on trusted hardware intelligence.
By combining Physical Layer Visibility, Hardware Access Control, and Rogue Device Mitigation, organizations can reduce the risk posed by unauthorized, unmanaged, and compromised devices while strengthening their overall security posture.
Ready to secure every connected assets in your network?
Talk to a Sepio expert and discover how Zero Trust Device Security helps verify device identity, eliminate hardware blind spots, and protect critical assets from rogue device threats.