FIN7’s BadUSB Attacks Highlight Two Critical Organizational Vulnerabilities
The criminal group FIN7 had been mailing malware-ridden USBs to various entities in the transport, insurance, and defense industries under the guise that they originated from a trusted source, such as Amazon and the US Department of Health and Human Services. Those from the former were supposedly gift vouchers, while the latter claimed to include new COVID guidelines.
FIN7’s BadUSB attacks serve as a reminder of two key vulnerabilities present in all organizations: human trust and limited asset visibility. Let’s explore them below.
The Human Factor Behind BadUSB Attacks
The BadUSB attack first exploited one of enterprises’ greatest weaknesses: people.
The malicious USBs appeared to have come from a legitimate source, thus gaining the recipient’s trust. The accompanying letters also played on human emotions, such as fear and greed, taking over any cautionary instincts.
The seemingly benign USB drive further alleviated any potential suspicion. After all, USB drives are common in the workplace, and employees are accustomed to connecting peripherals and removable media to their computers. A drive that appears to come from a trusted source is therefore less likely to raise suspicion.
Social Engineering and USB Threats
Social engineering is a key component of many cyberattacks. Hardware-based attacks require physical access to the target entity, and employee carelessness and negligence can make social engineering an effective tool for gaining that access.
As FIN7 demonstrated, social engineering played an important role in the success of the attacks. Employees can be an important barrier between a perpetrator and its target, demonstrating the ongoing need for employee cybersecurity training.
And while enterprises are aware of this need, with many undertaking actionable steps to address it, human error will always remain a weakness. Training is important, but it is not a silver bullet.
To mitigate staff carelessness, enterprises implement robust cybersecurity strategies, typically comprised of various policies, regulatory compliance, and security software.
Surely, then, enterprises have a security tool that identifies the BadUSB as a rogue device once it connects to an endpoint? Wrong.
And this brings us to the second vulnerability exploited in the BadUSB attack: asset visibility.
The BadUSB Visibility Gap
BadUSB attacks are specifically designed to evade traditional security controls by impersonating trusted Human Interface Devices (HIDs). Through firmware manipulation, a BadUSB attack can appear legitimate while executing unauthorized actions in the background. Since many security tools lack visibility into the hardware layer, detecting a BadUSB attack and other forms of hardware spoofing can be extremely challenging. This creates blind spots that hackers can exploit to gain unauthorized access, execute commands, or compromise sensitive systems.
Instead, security tools may recognize the hardware based on how it presents itself to the operating system. If it appears to be a familiar peripheral, such as a keyboard, it may not immediately trigger a security alert.
This is one of the key challenges of a BadUSB attack.
The threat is not necessarily a malicious file stored on the USB. The device itself can be manipulated to behave differently from what the user expects.
This is also why BadUSB should not be viewed simply as another form of malware delivered through removable media. The hardware can become part of the attack itself.
The Challenge of Detecting a BadUSB Attack
Once an employee has been successfully targeted through social engineering and subsequently connects the BadUSB to an endpoint, the organization may have limited visibility into what has actually been connected.
In some instances, the enterprise may not even know it has fallen victim to an attack.
When a rogue device is used to facilitate malware or ransomware, the organization may eventually recognize that it has suffered a security incident. However, it may not immediately realize that a rogue USB device was involved.
The situation becomes even more difficult when the hardware is used for reconnaissance, espionage, or data theft. In these cases, there may be no obvious indication that the physical hardware was responsible, making these types of attacks particularly difficult to detect.
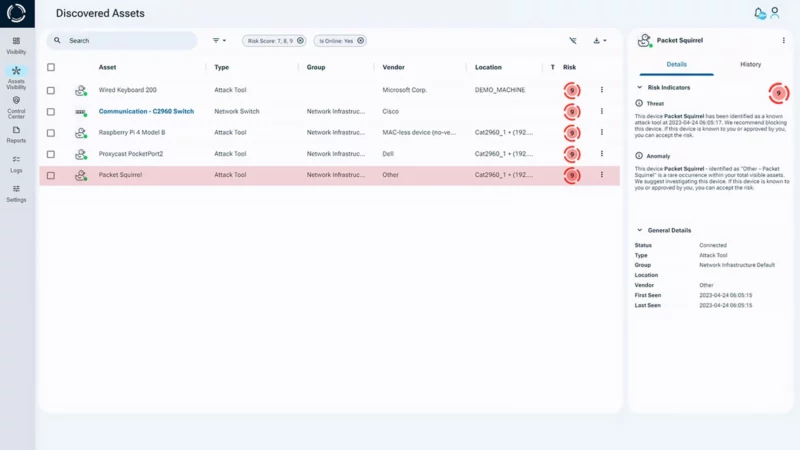
You Can Not Protect What You Can Not See
The BadUSB is just one of many rogue devices used to carry out malicious activities. These hardware-based attacks highlight that anything connected to an endpoint or network can potentially introduce risk.
While organizations can invest in cybersecurity training to increase employees’ awareness about the devices they are using, relying on employee awareness alone is not enough.
Organizations also need visibility into the hardware connecting to their systems.
This is particularly important because a device can appear legitimate to the operating system while still being unauthorized or manipulated.
Modern security frameworks increasingly recognize the importance of monitoring and controlling hardware additions. MITRE ATT&CK, for example, includes Hardware Additions as a technique and provides detection approaches for suspicious USB and other external devices.
Can Zero Trust Protect Against BadUSB Attacks?
Zero Trust is built around a simple principle: never trust, always verify. But applying that principle to users, applications, and endpoints is not always enough. What happens when the physical device itself cannot be trusted?
A BadUSB can look like a legitimate keyboard or other trusted device while behaving maliciously. In the FIN7 attacks, malicious USB devices were designed to act as keyboard emulators and send commands to the victim’s computer.
This highlights an important gap in traditional security controls: detecting a connection does not guarantee that the underlying hardware can be trusted.
Extending Zero Trust to Hardware
That is where hardware trust comes in. It means verifying the physical device itself rather than simply accepting what it reports about its identity or type. The goal is to determine whether it is legitimate, authorized, and safe to connect before allowing it to interact with the environment.
This extends the Zero Trust principle to the hardware layer. The approach is often referred to as Zero Trust Hardware Access (ZTHA): discover the hardware, verify its identity and trustworthiness, assess the risk, and enforce the appropriate policy.
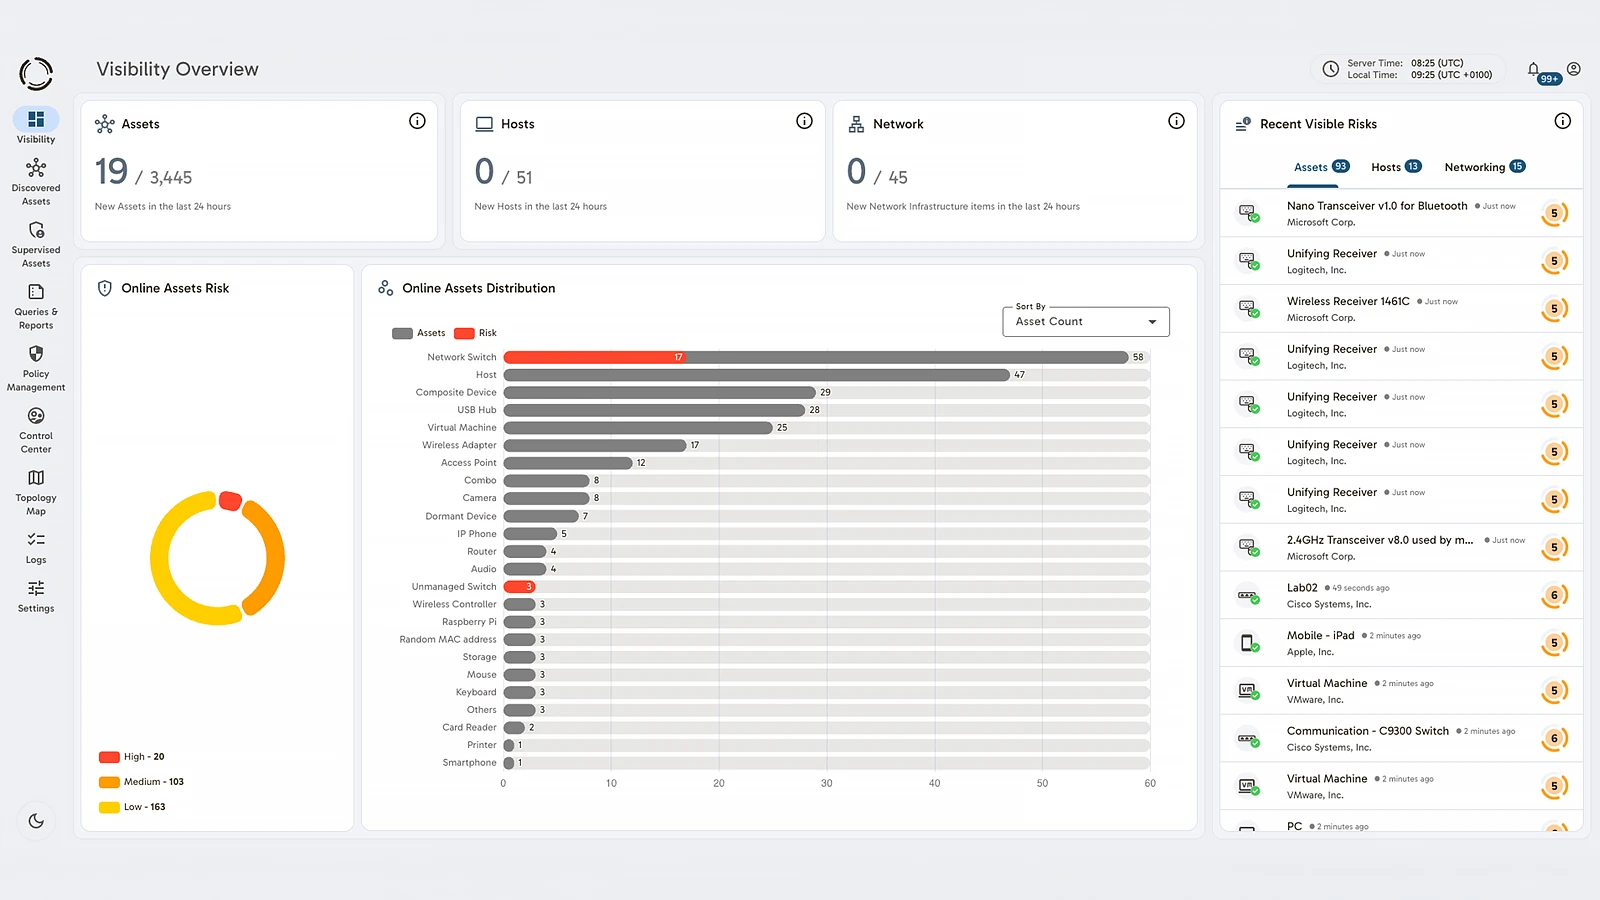
For BadUSB attacks, this distinction matters. A device may identify itself as a keyboard, but that doesn’t necessarily tell you whether it is an authorized keyboard or a malicious one pretending to be.
The question changes from “What does this hardware claim to be?” to “What is it actually?”
FIN7’s use of malicious USB devices shows why physical hardware can become an overlooked part of the attack surface. For more details on the campaign and how the attack was carried out, read the Security Affairs article.
BadUSB is a reminder that Zero Trust shouldn’t stop at the endpoint. Organizations also need visibility into the physical devices connecting to their environments, and the ability to determine whether those devices should be trusted.
Talk to an expert