ATM Cybersecurity is critical for protecting automated teller machines (ATMs) against cyberattacks, malware, rogue devices, and hardware-based threats. Because ATMs provide direct access to financial systems and cash, they remain attractive targets for cybercriminals seeking financial gain.
Effective ATM security requires more than traditional software-based protection. Attackers can exploit software vulnerabilities, network connections, USB interfaces, and physical access to compromise ATM infrastructure. Financial institutions therefore need comprehensive ATM cybersecurity solutions that address endpoint, network, and physical-layer threats while protecting the integrity of their ATM environments.
ATM cyberattacks can result in direct financial losses while also affecting the reputation and customer trust of financial institutions. As attack techniques continue to evolve, maintaining visibility into connected assets and detecting unauthorized hardware are important components of a strong ATM security strategy.
Types of ATM Cyberattacks and Security Threats
ATM cyberattacks can take various forms, reflecting the diverse tactics cybercriminals use to compromise these financial machines. Some common types of cyberattacks on ATMs include:
ATM Specific Malware
Malicious software (Malware) can be injected directly into an ATM, either through physical access to the machine or by exploiting vulnerabilities in its software. Once installed, the malware can manipulate the ATM’s operations for fraudulent transactions (i.e., CutletMaker, Ploutus D, ATM Proxy).
Hardware-Based Attack – ATM Black Box Attacks
Black box attacks involve connecting an external device to the ATM’s internal hardware to override its software and force the machine to dispense cash. These attacks typically require physical access and are often paired with malware to bypass security controls.
ATM Network Security and Network Implant Attacks
Hackers utilize rogue devices, such as network implants, to intercept or manipulate ATM communications with financial institutions. These devices are often undetectable by standard ATM security software, enabling cybercriminals to execute remote attacks and maintain anonymity.
Rogue Devices and ATM Cyber Security
Rogue devices can play a significant role in ATM cyberattacks, including ransomware and man-in-the-middle (MiTM) attacks conducted through USB or Ethernet interfaces. These hardware-based threats can operate at the physical layer, making them difficult for traditional ATM security software and network security solutions to detect.
For example, an attacker can attach a spoofed peripheral to an ATM’s cash dispenser and send unauthorized cash-dispensing commands, bypassing the need for a legitimate card or transaction authorization. This type of attack is known as an ATM black box attack and typically requires physical access to the ATM’s internal components.
As gaining direct physical access becomes more difficult, attackers can turn to external network implants. These rogue devices can enable remote ATM attacks, increasing attacker anonymity and presenting an additional challenge for ATM cybersecurity.
Network implants are often based on modified off-the-shelf hardware, such as cellular routers configured to operate in transparent or bridge mode. Because they can operate without a Layer 2 MAC address presence, they may evade conventional Network Access Control (NAC) and Intrusion Detection System (IDS) solutions. This highlights the importance of physical-layer visibility and the ability to identify hardware that traditional network security tools may not detect.
ATM Endpoint Security and Network Visibility
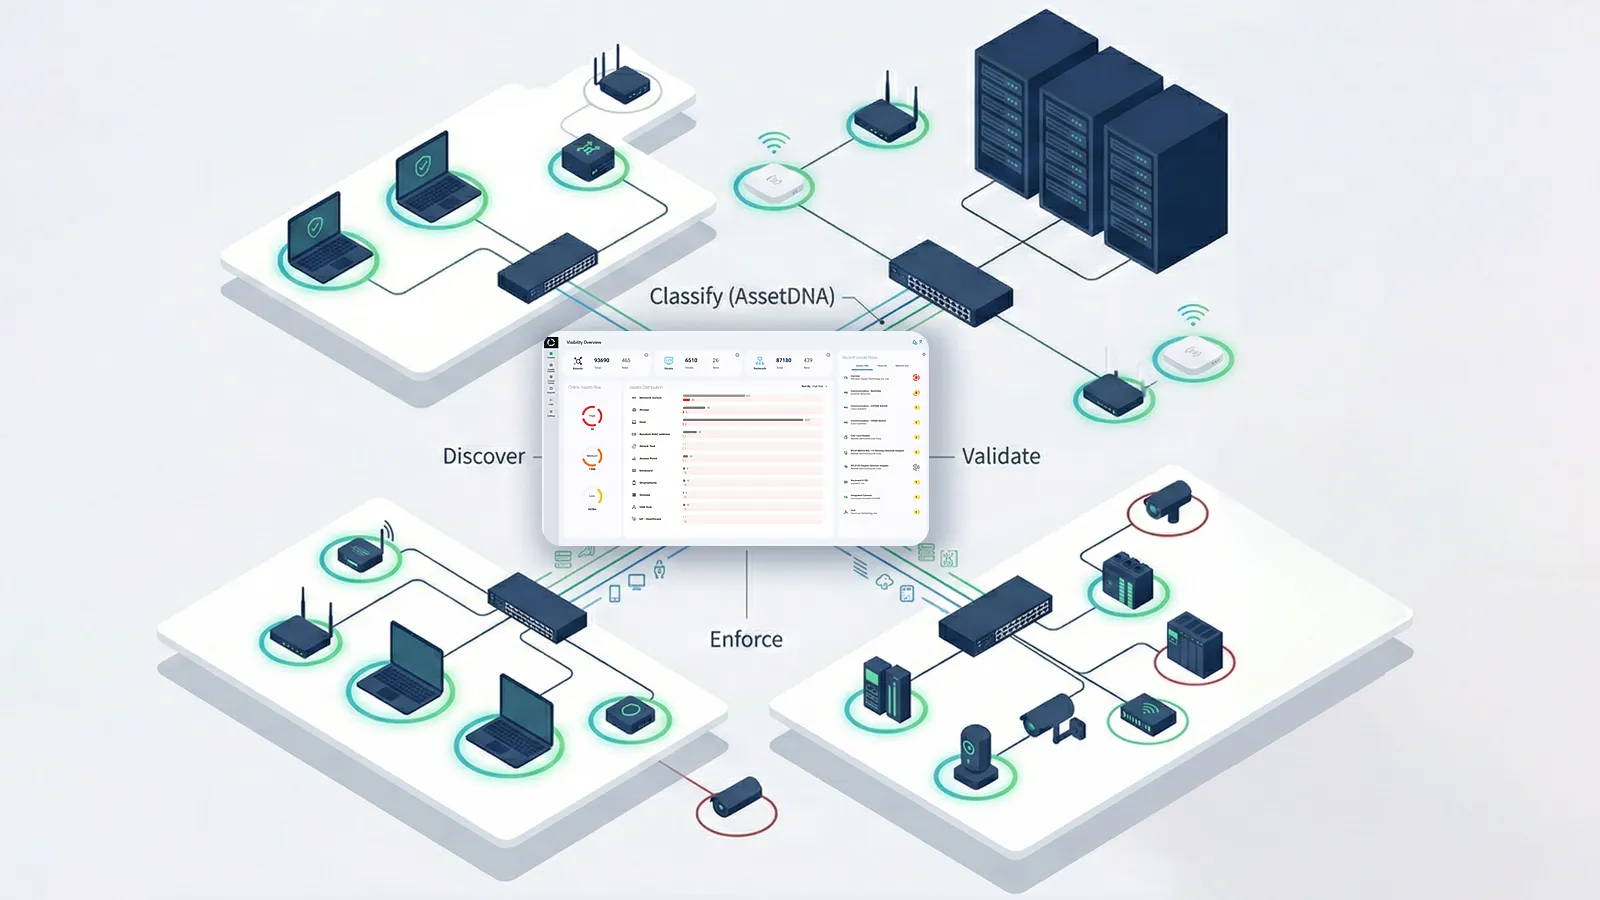
ATM endpoint security depends on comprehensive visibility into the hardware assets and peripherals connected to ATM infrastructure. Without this visibility, attackers can exploit blind spots through USB and network interfaces, introducing rogue devices, network implants, and other hardware-based threats that traditional security controls may overlook.
These blind spots can weaken the enforcement of hardware access policies and increase the risk of ATM cyberattacks, including attacks involving ransomware. Organizations therefore need continuous visibility into connected hardware assets across endpoint and network interfaces.
Attackers can exploit these blind spots using techniques such as USB Human Interface Device (HID) emulation and physical-layer network implants. These techniques may bypass traditional security mechanisms, highlighting the importance of physical-layer visibility for strengthening ATM endpoint and network security.
ATM Endpoint and Network Security with Sepio
ATM endpoint and network security require more than visibility into connected devices. Financial institutions need to know what hardware is connected, verify what each device actually is, understand the risk it represents, and determine whether it should be trusted.
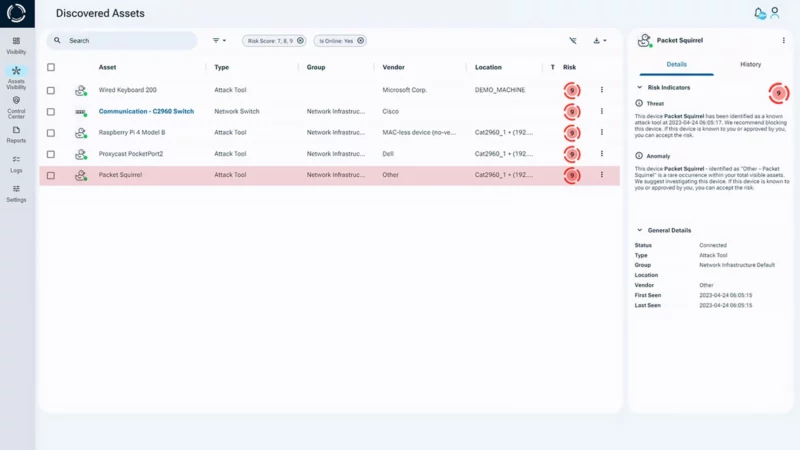
Sepio brings AI-powered Hardware Superintelligence to ATM cybersecurity by combining physical-layer intelligence with Hardware AssetDNA to establish verified device truth. Rather than relying solely on identifiers and information reported by a device, Sepio helps identify hardware based on what it physically is, exposing rogue, spoofed, hidden, and unauthorized devices that traditional cybersecurity controls may overlook.
This intelligence enables financial institutions to continuously assess connected hardware against expected identity, context, posture, and security policies. Potential risks and anomalies can then be translated into policy-based actions, helping security teams contain, block, isolate, escalate, or remediate threats based on verified hardware intelligence.
Through Zero Trust Hardware Access (ZTHA), Sepio extends Zero Trust principles to the hardware layer of ATM environments. Hardware trust is not assumed based on what a device claims to be. Instead, it is continuously established through verified device identity, context, posture, and risk, helping financial institutions strengthen protection against rogue devices, network implants, spoofed peripherals, and other hardware-based threats.
Strengthen Your ATM Cybersecurity
Achieve full visibility into every known and shadow asset within your ATM ecosystem. Proactively prioritize threats and mitigate risks with confidence. Discover how Sepio’s patented technology empowers you to uncover hidden hardware-based threats and take control of your ATM cybersecurity posture.
Schedule a demo and see how Sepio can help you eliminate blind spots, enforce granular security policies, and safeguard your financial infrastructure from physical-layer ATM cyber attacks.
Read the ATM Cyber Security white paper (pdf)