What are Hardware Attacks?
Hardware attacks in cybersecurity are among the most overlooked threats facing organizations today. Instead of targeting software alone, hackers can exploit physical devices, hardware interfaces, and implicit trust in connected equipment to circumvent or evade traditional security controls such as Network Access Control (NAC), Endpoint Detection and Response (EDR), and Intrusion Detection Systems (IDS). These attacks may involve malicious hardware disguised as everyday devices, including USB peripherals, chargers, keyboards, or network adapters. Because this malicious hardware can appear legitimate to traditional security controls, hackers may use it to gain access to systems and networks without immediately raising suspicion.
Traditional security tools focus primarily on software, network traffic, and user activity. However, the physical hardware connecting to these environments can receive less attention. This creates a hardware security blind spot where hardware attacks, rogue hardware, and malicious hardware may remain undetected for extended periods. Addressing this gap requires organizations to extend cybersecurity to the hardware layer, identify unauthorized or manipulated hardware, and detect hardware-based threats before they can be used to compromise systems and networks.
As organizations become increasingly dependent on connected devices and peripherals, hardware-based attacks present a growing security risk. Effective hardware security requires more than knowing which devices are connected. Organizations need to establish and continuously verify hardware identity, assess device characteristics and behavior, and detect unauthorized or manipulated hardware that may otherwise appear legitimate. By validating the hardware itself, organizations can better identify hardware vulnerabilities and reduce the risk of hardware-based attacks.
Hardware Attacks in Cybersecurity
Human behavior can play an important role in enabling hardware attacks. Employees may connect unfamiliar or unauthorized devices to corporate systems without recognizing the potential security risks. This can create opportunities for hackers to exploit implicit trust in physical hardware and gain access to systems or networks.
Unlike traditional cyberattacks that rely on software vulnerabilities, hardware attacks often exploit human behavior. Hackers take advantage of curiosity, convenience, and a lack of awareness by introducing unauthorized devices into an environment. Once connected, these devices can potentially interact with systems, intercept communications, or establish a foothold within an environment.
Hardware attacks can be particularly difficult to detect because the malicious hardware may appear legitimate to both users and traditional security controls. A seemingly ordinary peripheral can perform malicious functions without immediately revealing its true purpose. As organizations continue to expand their digital infrastructure and rely on increasingly connected hardware, securing the physical layer has become an important part of a comprehensive cybersecurity strategy.

Hardware Attacks Through Everyday Devices
Hardware attacks do not always involve sophisticated or visibly malicious equipment. Hackers can hide malicious hardware inside everyday peripherals, such as keyboards, mice, USB devices, and network adapters. Because these devices can resemble legitimate hardware, they may be trusted by users and recognized by security systems as ordinary peripherals.
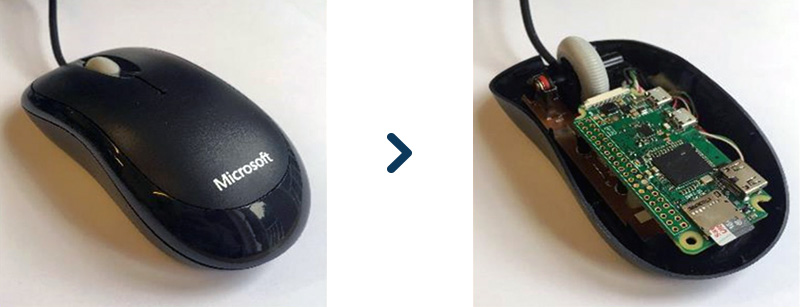
A Raspberry Pi is a small single-board computer that can be configured for many legitimate applications. Its compact size and connectivity options can also make it suitable for unauthorized hardware deployments. When configured as an hardware attack tool, a Raspberry Pi can be used for activities such as network reconnaissance, traffic interception (MiTM), or other hardware-based attacks, depending on how it is configured.
A BadUSB device provides another example of how malicious hardware can disguise itself as a legitimate peripheral. A device may identify itself to a host computer as a keyboard, mouse, or other trusted USB device while performing unauthorized actions. This demonstrates a fundamental hardware security challenge: the device presented to the operating system may not reveal the true security intent of the physical hardware.
Using an iPhone Charger as an Attack Tool
The “NinjaCable” is a USB hardware attack tool that looks just like a regular iPhone charger, but it can cause serious harm. The idea isn’t new. Its design is based on an NSA tool called COTTONMOUTH.
Hackers use the NinjaCable to take advantage of human trust. It works like a normal charger, while secretly launching attacks like malware or stealing data in the background.
First, no one questions an iPhone charger. If your phone dies at work, you’ll likely grab the nearest charger without thinking. You rarely stop to ask if it could be a harmful device.
Second, smartphones are always linked to both work and personal accounts. This gives attackers more ways to strike from almost anywhere. Instead of sneaking a NinjaCable into a secure office, they can now use public charging stations to launch their hardware attacks.
At charging stations, people often plug in their phones quickly, just thinking about getting power. But this can be risky. A tactic called “juice jacking” lets hackers steal personal or work data from the device. As phones connect more to both personal and work systems, hidden hardware threats become even more dangerous.
The Threat of Malicious USB Thumb Drives
Malicious USB drives are another well-known example of hardware-based attacks. From the outside, a malicious USB thumb can look identical to an ordinary storage drive, making it difficult for users to determine whether the hardware is trustworthy simply by examining its appearance.
Attack tools such as the Rubber Ducky demonstrate how USB devices can be designed to emulate a keyboard and automatically send keystrokes to a connected computer. Depending on its configuration and the security controls in place, the hardware can be used to execute commands or launch other malicious actions.
The security challenge is not limited to whether a USB drive contains malware. The physical hardware itself may be designed to impersonate another type of peripheral, creating a gap between what the hardware appears to be and what it is capable of doing.
How Malicious Hardware Evades Detection
Rogue devices are especially dangerous because they look harmless. They stay hidden from firewalls and intrusion detection systems. They also bypass any human-based authentication checks. Once connected, they can give hackers full access to an organization’s systems.
Even the most advanced cybersecurity models, like Zero Trust Architectures, often fail to stop hardware threats. These attacks take advantage of a core weakness: Zero Trust relies on verifying identity and behavior. But rogue hardware can fake identities and operate without raising any alarms.
Hardware attack tools are discreet, allowing them to move freely within an organization. As a result, they break key Zero Trust principles like microsegmentation and least privilege access. Moreover, they do not raise red flags to the human eye, avoid detection by traditional cybersecurity tools, and can carry out many harmful actions.
But if you think all hope is lost, think again. Specialized solutions do exist to defend against these hardware threats. While no system is entirely invulnerable, proactive, cybersecurity measures can significantly strengthen your organization’s defensive posture and close the gap traditional tools leave behind.
Detecting Hardware Attack Tools
Sepio has developed a solution to provide a panacea to the gap in device visibility through physical layer fingerprinting. As the leader in Rogue Device Mitigation (RDM), Sepio finds, detects, and manages all peripherals. No asset is left unmanaged.
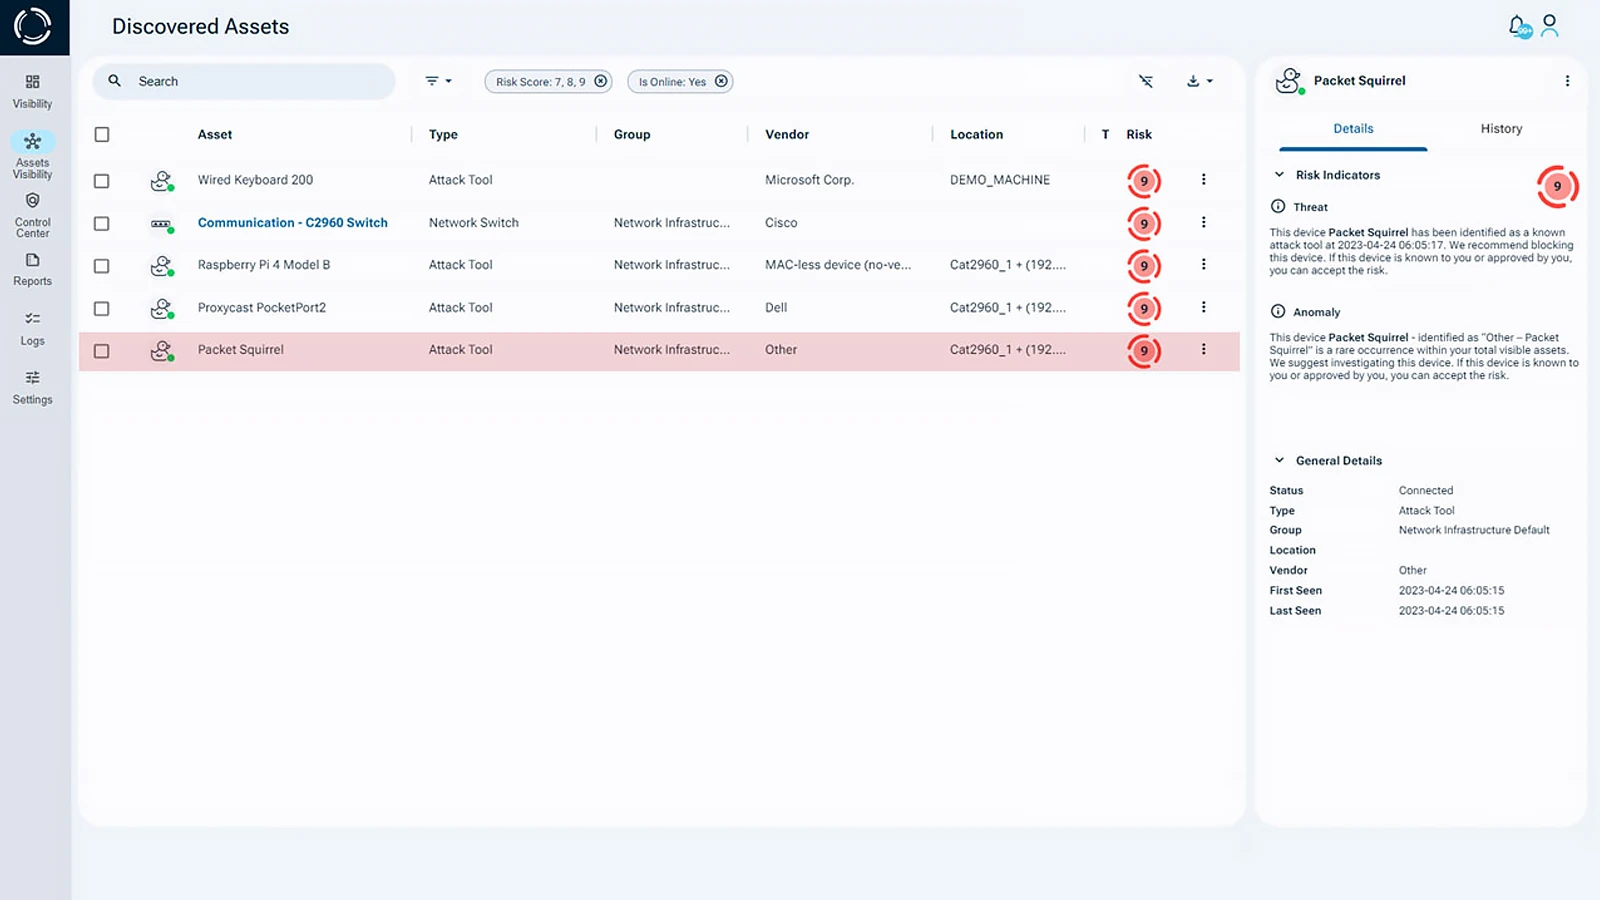
Sepio’s policy enforcement and mitigation features block unauthorized devices instantly. This helps prevent human error and removes the need to constantly watch over network devices. Even careful employees can miss these hardware threats. That’s why automated hardware protection is essential.
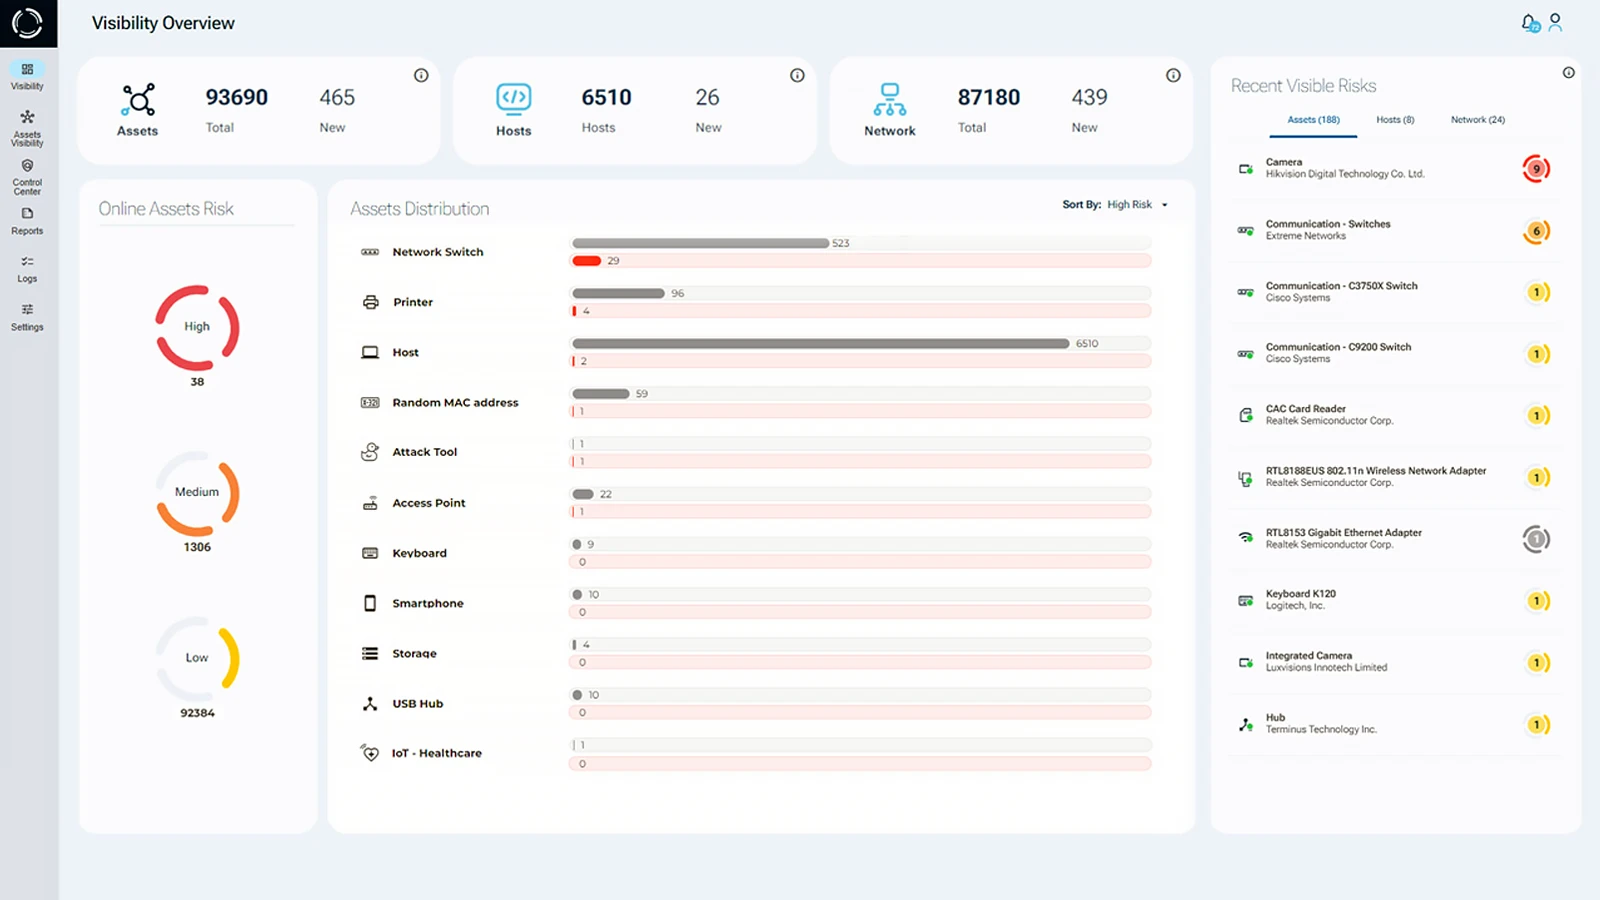
Additionally, Sepio’s deep visibility capabilities and integration with existing tools, such as NAC, EPS, and SIEM, ensure that organizations maximize their cybersecurity investments. As a result, with Sepio, clients benefit from a Zero Trust Hardware Architecture (ZTA) approach.
Network and Endpoint Hardware Security
Sepio doesn’t scan network traffic or use discovery tools. That means it won’t touch any private or sensitive data. Setup is quick and easy. In just 24 hours, we help reduce employee mistakes and strengthen your company’s cybersecurity. Your employees are your biggest strength, but also a big risk. Sepio helps you lower that risk with a powerful hardware cybersecurity solution.
Secure your organization against hardware attacks with Sepio’s patented technology. Schedule a demo to see how we enhance your cybersecurity hardware protections.
Talk to an expert