What is Hardware Security?
Hardware security is the practice of protecting physical devices, such as servers, routers, USB devices, laptops, IoT assets, and industrial controllers, from tampering, unauthorized access, and cyberattacks. As these devices form the foundation of modern IT and operational environments, securing hardware is essential to maintaining a strong cybersecurity posture.
Effective hardware security ensures that connected devices and the data they process remain trusted, available, and protected against compromise. Without adequate protection, rogue devices, malicious peripherals, and hardware-based attack tools can bypass traditional security controls, creating opportunities for unauthorized access, data theft, operational disruptions, and supply chain attacks.
In environments that rely on cyber-physical systems (CPS), hardware security is particularly important. Organizations must protect not only their IT infrastructure but also the physical devices that connect digital networks with industrial equipment and operational processes. Securing these interconnected environments requires visibility into and control over every connected hardware asset.
This guide explores common hardware security threats, including supply chain attacks, hardware implants, and unauthorized peripherals. It also examines how organizations can strengthen hardware security through comprehensive asset visibility, continuous hardware identification, and proactive risk mitigation with Sepio’s Zero Trust Hardware Access (ZTHA) platform.
Hardware Security Measures for Modern Enterprises
Effective hardware security requires organizations to know what devices are connected to their networks, verify their identities, understand the risks they pose, and control which devices can access critical resources. Rogue devices, unauthorized peripherals, and malicious hardware attack tools can bypass traditional security controls, creating risks such as unauthorized access, data theft, and operational disruptions.
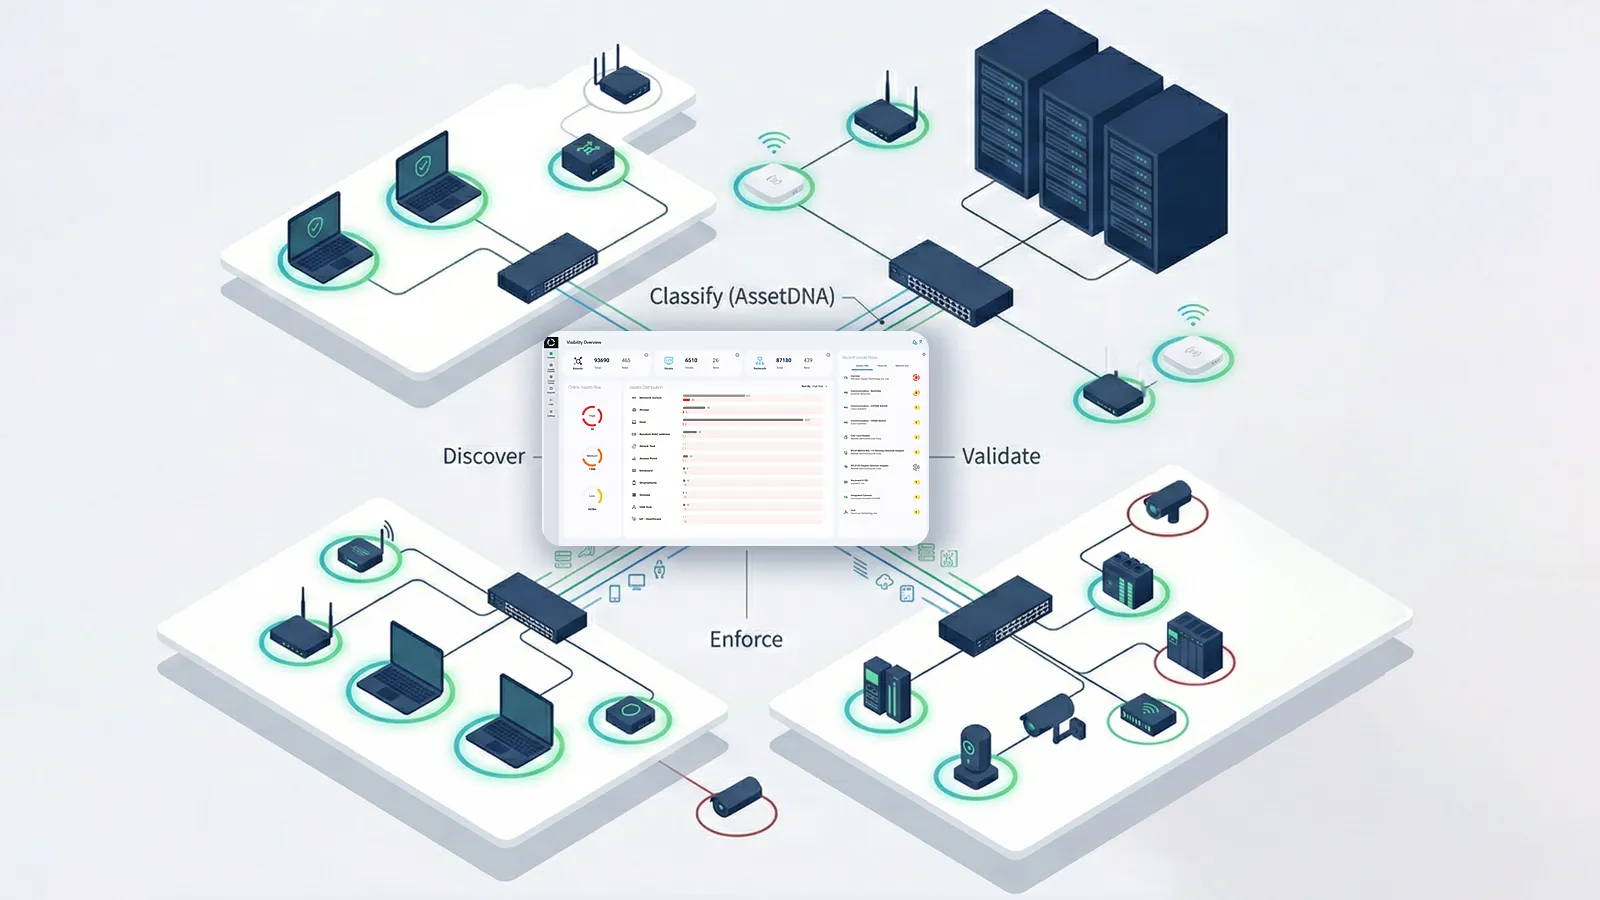
Sepio addresses these risks through its Zero Trust Hardware Access (ZTHA) approach. Instead of relying only on network activity or information reported by devices, Sepio uses patented AssetDNA™ technology to identify hardware based on its physical characteristics. This allows organizations to discover and identify all connected devices, including managed, unmanaged, hidden, and potentially malicious assets across IT, OT, and IoT environments.
Sepio’s Hardware Superintelligence builds on this visibility by turning hardware data into useful security insights. By combining AssetDNA™, machine learning, and threat intelligence, the platform helps security teams understand what each device is, identify suspicious hardware, and assess the risks it may introduce. This makes it easier to detect rogue devices, spoofed hardware, and other threats that traditional security tools may miss.
With Zero Trust Hardware Access, Sepio goes beyond discovering devices. The platform continuously checks hardware identities, assesses device risks, and applies security policies. Unauthorized, non-compliant, or malicious devices can trigger alerts or be automatically blocked from accessing critical resources. This helps organizations reduce hardware-related risks, protect their IT and OT environments, and ensure that only trusted devices connect to their networks.
Hardware Asset Inventory and Visibility
Maintaining an accurate hardware inventory is essential for understanding an organization’s attack surface. However, many organizations lack visibility into every device connected to their networks, particularly unmanaged, forgotten, or unauthorized hardware.
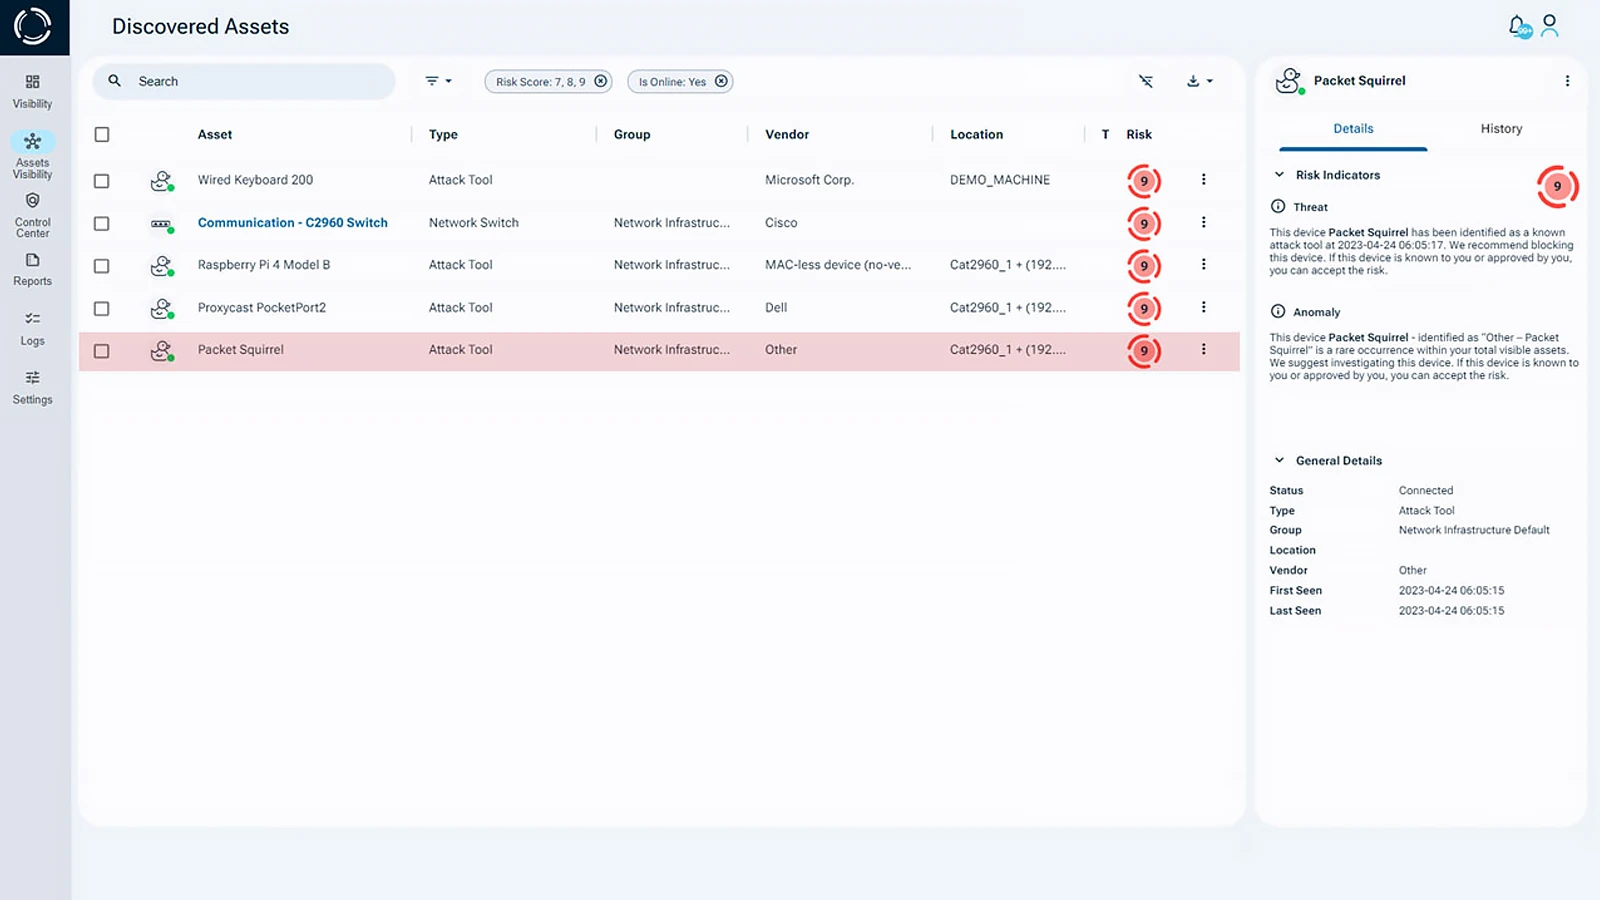
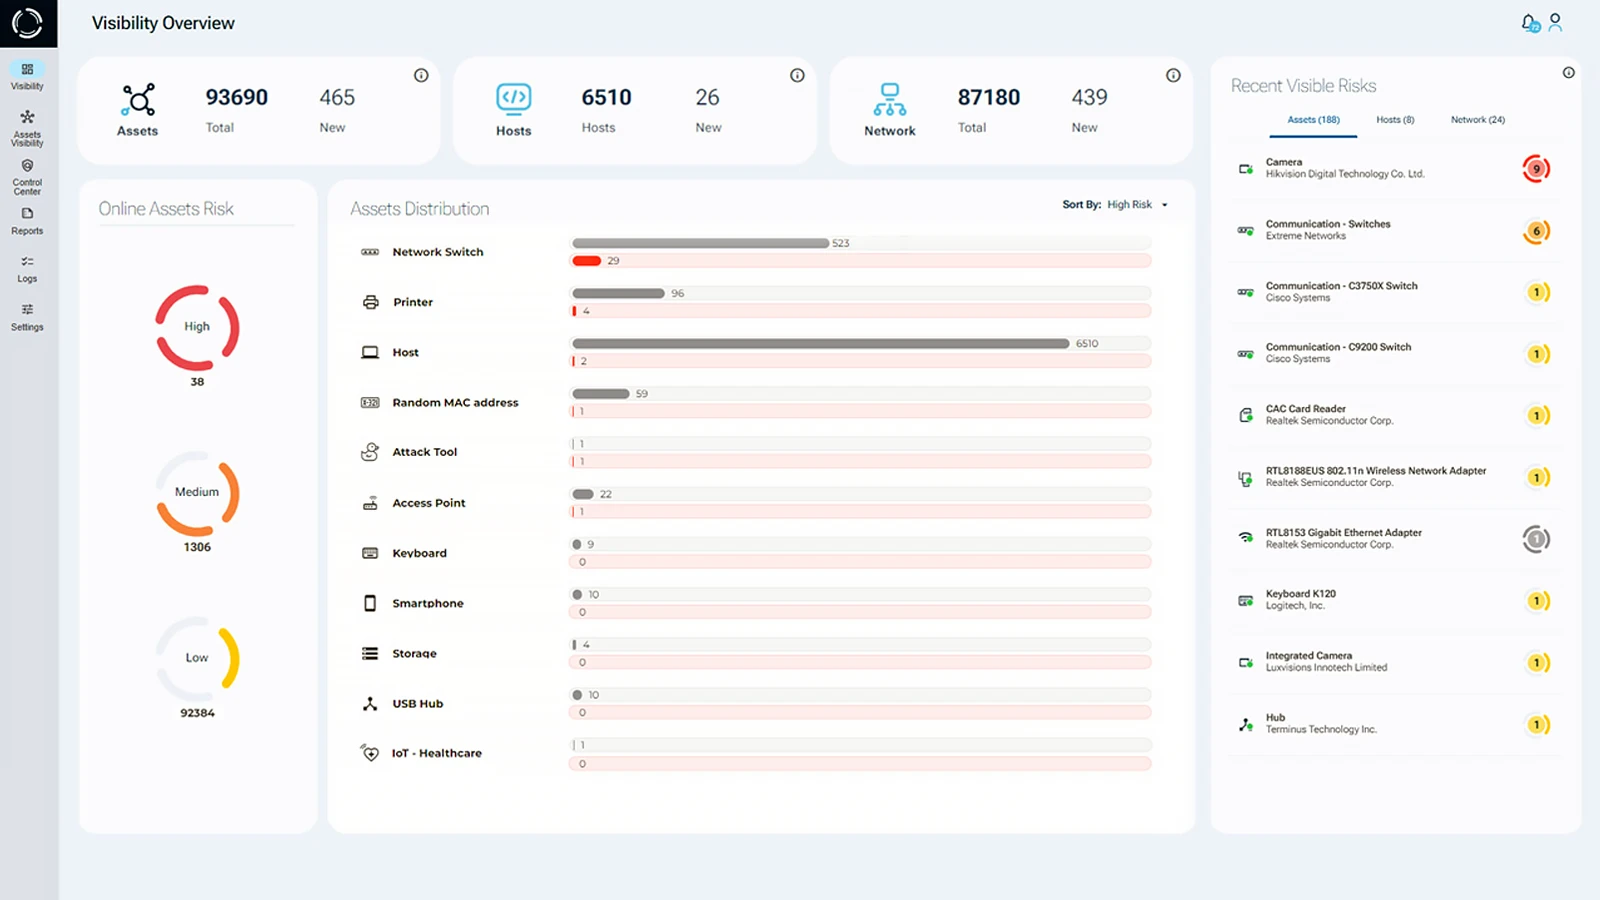
Sepio provides a comprehensive inventory of connected assets across IT, OT, IoT, and IoXT environments, including:
- Managed and unmanaged devices: Gain visibility into assets, including shadow IT devices that may not appear in existing inventories.
- Hidden hardware: Discover devices that are difficult to identify using traditional asset management tools.
- Unauthorized devices: Identify hardware that does not belong in the organization’s environment.
Beyond maintaining an up-to-date inventory, Sepio helps organizations understand the risk associated with each connected asset. Its hardware risk scoring system assigns each device a score from 1 to 9, helping security teams distinguish low-risk assets from those requiring immediate attention.
Common Hardware Security Threats and Attacks
Hardware attacks can take many forms, from malicious USB devices to hidden network implants. Unlike traditional cyberattacks that target software or operating systems, hardware-based attacks exploit physical devices and their connections to gain unauthorized access, steal information, or disrupt operations.
Some attacks begin with social engineering. For example, attackers may trick employees into plugging in malicious BadUSB devices that imitate keyboards or other trusted peripherals. Once connected, these devices can execute commands, capture information, or introduce malware. Employee awareness and security training can help reduce these risks.
Other threats involve rogue hardware designed to look like legitimate equipment. Examples include USB Human Interface Device (HID) emulation tools, malicious peripherals, and hidden physical-layer network implants. Because these devices may appear legitimate, they can go unnoticed by traditional security solutions, including Network Access Control (NAC), Intrusion Detection Systems (IDS), and conventional IoT security tools.
These threats highlight an important gap in enterprise cybersecurity: protecting networks and software is not enough if connected hardware remains unchecked. Organizations need to account for the physical devices connecting to their environments and understand the risks they may introduce.
Sepio helps address this challenge by identifying rogue and unauthorized hardware that traditional security tools may overlook. Through hardware-level identification and risk assessment, organizations can detect suspicious devices and take action before they compromise critical systems.
Understanding these threats is the first step toward improving hardware security and protecting enterprise environments against hardware-based attacks.
The Five Pillars of Zero Trust Hardware Access
Traditional Zero Trust approaches focus primarily on users, applications, and network access. However, connected hardware also needs to be identified, verified, and trusted before it is allowed to access critical resources. This approach builds on the principles outlined in the NIST Zero Trust Architecture.
Sepio extends Zero Trust to the hardware layer through its Zero Trust Hardware Access (ZTHA) framework, built around five pillars: Discover, Verify, Validate, Score, and Enforce.
- Discover: Identify every connected asset across network, endpoint, peripheral, IT, OT, and IoT environments, including unmanaged and hidden devices.
- Verify: Establish the true identity of each device using Sepio’s patented AssetDNA™ technology and physical-layer intelligence.
- Validate: Check whether each device matches its expected identity, role, location, ownership, and security policies.
- Score: Assess hardware risk based on device identity, security posture, vulnerabilities, and business context, helping organizations prioritize potential threats.
- Enforce: Apply security policies through alerts, access restrictions, isolation, blocking, and integration with existing security tools.
Together, these five pillars help organizations move beyond traditional asset visibility toward continuous hardware trust. By identifying devices, checking their identities and security status, assessing their risks, and enforcing access policies, Sepio helps ensure that only trusted hardware can access critical enterprise resources.
Strengthening Enterprise Hardware Security
Gain a comprehensive understanding of your enterprise’s hardware cybersecurity posture with Sepio platform. Uncover weaknesses, make informed adjustments, and improve your overall security posture. Explore the power of Sepio and the valuable risk insights it provides for improved network hardware cybersecurity.
Schedule a demo. It will help you understand how to use Sepio’s patented technology to gain control of your asset risks.
Talk to an expertFrequently Asked Questions
Hardware security refers to the technologies, controls, and practices used to protect physical devices and connected hardware from unauthorized access, tampering, compromise, or malicious activity. It helps organizations ensure that only trusted devices can interact with their networks and systems.
Hardware security is important because every cybersecurity strategy relies on trusted devices. If attackers can introduce rogue or compromised hardware into an environment, they may bypass traditional security controls, gain unauthorized access, steal data, or disrupt operations.
Physical hardware security focuses on protecting devices from direct physical attacks, tampering, theft, and unauthorized connections. This includes securing endpoints, network-connected devices, USB peripherals, IoT assets, and other hardware that could be used as entry points into the organization.
Hardware-based security uses hardware technologies and trusted device characteristics to strengthen security controls. By leveraging hardware-level validation and protection mechanisms, organizations can improve resilience against attacks that software-based defenses alone may miss.
Common hardware security threats include rogue devices, hardware implants, malicious USB devices, unauthorized peripherals, network impersonation attacks, supply chain compromises, and devices that conceal their true identity. These threats can create blind spots that traditional security tools may not detect.
Organizations can improve hardware security by maintaining complete visibility into connected assets, enforcing device access policies, monitoring for unauthorized hardware, reducing unmanaged device exposure, and continuously verifying device identities throughout their lifecycle.
Cyber security hardware solutions help organizations discover, identify, monitor, and control hardware assets across their environments. These solutions complement traditional cybersecurity controls by addressing risks at the physical layer and improving visibility into connected devices.
Zero Trust Hardware Access (ZTHA) extends Zero Trust principles to hardware by verifying the true identity of every connected device before granting access. Instead of automatically trusting hardware, ZTHA enables organizations to continuously validate devices, detect rogue assets, and enforce hardware-based access policies, reducing risks across enterprise environments.