Moving Target Defense (MTD) cybersecurity represents a shift in how organizations approach data security and protection against cybersecurity risks. Unlike traditional static defense mechanisms, Moving Target Defense cybersecurity focuses on dynamically changing the attack surface to make it more challenging for adversaries to understand, track, and exploit vulnerabilities.
One effective tactic used in Moving Target Defense cybersecurity is the randomization of MAC addresses, which can make it more difficult for potential attackers to consistently identify and track devices. However, this approach can also introduce new challenges for asset visibility, particularly when organizations rely on network identifiers to identify and track connected devices.
Effective Moving Target Defense therefore requires organizations to maintain reliable visibility into the assets they are protecting, even as their network characteristics change. This article explores the implications of MAC address randomization within the context of Moving Target Defense cybersecurity and how organizations can maintain reliable asset visibility in dynamic network environments.
What is Moving Target Defense (MTD)?
Moving Target Defense (MTD) cybersecurity is a dynamic strategy that aims to make an environment less predictable for potential attackers. Rather than relying solely on static configurations and identifiers, an Moving Target Defense strategy introduces controlled changes into the network environment, making it more difficult for hackers to identify, track, and exploit potential targets.
MAC address randomization is one example of this approach. MAC addresses have traditionally been used as network-level identifiers for devices. By changing or randomizing these addresses, organizations can make it more difficult for attackers to consistently track or profile individual devices.
However, the same change that increases uncertainty for attackers can create challenges for defenders. When a device’s network identifier changes, traditional asset-management and security systems may have difficulty maintaining continuity between the device’s previous and current identities.
This creates an important requirement for Moving Target Defense cybersecurity: organizations need to be able to distinguish between a changing network identity and the underlying asset it represents.
MAC Address Randomization: Balancing Security and Asset Visibility
While MAC address randomization can provide an additional layer of security, it also introduces challenges for asset visibility. MAC addresses have traditionally played an important role in asset tracking and network management. When these identifiers change, organizations may find it more difficult to maintain an accurate and continuous view of their connected devices.
The challenge is therefore not simply knowing which MAC address is currently being used. Organizations also need to determine whether a newly observed network identity represents a new device or the same underlying physical asset.
Maintaining reliable asset visibility is particularly important when implementing Moving Target Defense. Organizations need sufficient visibility into their environment to understand which assets are present, identify authorized and unauthorized devices, and maintain asset identity as network characteristics change.
Anchoring Moving Target Defense Cyber Security in the Physical Layer
Moving Target Defense introduces a dynamic layer to traditional static security measures. With fluctuating MAC addresses, the physical layer of the network can provide a more stable reference for maintaining asset visibility. This refers to the actual hardware components, such as computers, servers, switches, routers, and even USB peripherals, that are physically connected to a network.
Because these physical assets remain relatively stable even when their network-level identifiers change, they can provide a persistent reference point for asset tracking and management. This allows organizations to maintain continuity in asset identity and distinguish between a device whose network identity has changed and a genuinely new device.
The Advantages of Physical Layer Anchoring in MTD Cybersecurity
- Persistent Hardware Identity: Physical properties and hardware characteristics can provide a reliable reference for tracking assets, even when network-level identifiers change.
- Enhanced Security: With physical layer visibility, organizations can better detect unauthorized or rogue devices and identify changes in their physical environment.
- Comprehensive Inventory Management: Focusing on the physical layer enables more accurate and continuous asset tracking, helping organizations maintain visibility and manage security risks in dynamic network environments.
Overcoming Challenges
- Real-Time Monitoring: As MAC addresses can change dynamically, with moving target defense, real-time monitoring becomes essential for keeping an up-to-date asset inventory and detect potential breaches or intrusion.
- Advanced Tools: The use of sophisticated asset management tools designed for dynamic environments can also facilitate better asset visibility.
- User Training: Additionally, educating staff on the new paradigm ensures that best practices are maintained. Even in an ever-changing Moving Target Defense (MTD cybersecurity) landscape.
Existing Cybersecurity Solutions Do Not Address Physical Layer Visibility
Existing security software solutions do not cover the Physical Layer (layer 1) of the OSI model . Without physical layer visibility, malicious devices, such as rogue devices or spoofed peripherals, can easily infiltrate the network undetected, heightening the security risks associated with a breach. Moreover, the absence of endpoint monitoring at this foundational layer exposes organizations to attacks that could compromise the integrity of their entire network.
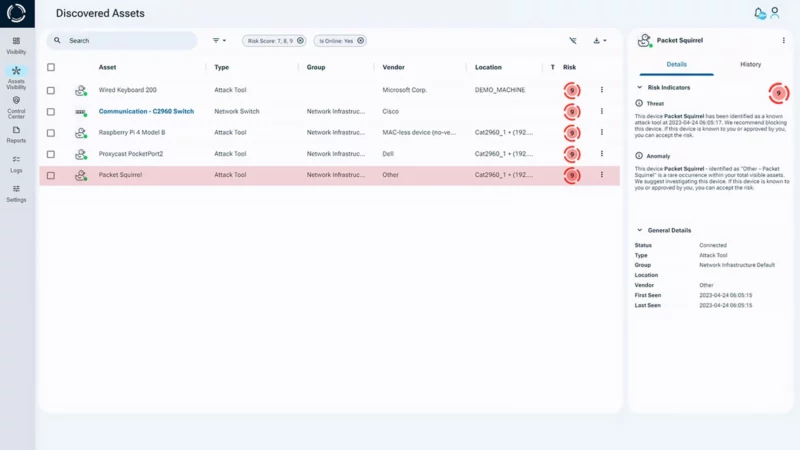
Moving Target Defense (MTD) and Asset Visibility
While MAC address randomization, offers a powerful strategy against modern cyber threats, it poses challenges for asset visibility. However, by focusing on the physical layer and adopting advanced asset management solutions, organizations can strike a balance between maintaining strong security measures and effective asset visibility. This approach helps mitigate the challenges posed by MTD and allows organizations to stay ahead of potential security risks.
In this ever-evolving landscape, anchoring security efforts in the physical layer provides a firm foundation for both cybersecurity and asset management, enabling organizations to combat threats from hackers and safeguard their network against ransomware and data breaches.
By employing this balanced approach, companies can continue to reap the benefits of Moving Target Defense (MTD cybersecurity). And mitigating the challenges posed by MAC address randomization, thereby achieving both robust defense and reliable asset visibility.
Strengthening Moving Target Defense Cybersecurity for Comprehensive Risk Mitigation
In this ever-evolving landscape, anchoring security efforts in the physical layer provides a firm foundation for both cybersecurity and asset management, enabling organizations to combat threats from hackers and safeguard their network against ransomware and data breaches.
By employing this balanced approach, companies can continue to reap the benefits of MTD cybersecurity while mitigating the challenges posed by MAC address randomization, thereby achieving both robust defense and reliable asset visibility.
Talk to an expert. Our team can help you understand how to use Sepio’s patented technology to gain control of your asset risks, ensuring robust data security and protection from hacker intrusions.