Strengthen SWIFT CSCF v2026 Compliance
with Trusted Hardware Visibility
SWIFT CSCF v2026 defines mandatory and advisory controls to secure the SWIFT environment, reduce cyber risk, and support compliance across financial institutions. Sepio enables complete visibility across your SWIFT environment, ensuring every device is known, authorized, verified, and continuously monitored.
Hardware Visibility Challenges in SWIFT Environments
Modern SWIFT environments are expanding across distributed infrastructure, multiple operational teams, and constantly changing device inventories. As a result, maintaining an accurate view of every connected devices inside secure zones becomes increasingly difficult.
These blind spots create real security risks by allowing unknown, unmanaged, rogue or spoofed devices to operate undetected. Risks that traditional cybersecurity tools may not fully detect or mitigate.
1. Unknown and Unauthorized Devices
Unidentified, unmanaged, or rogue devices can appear across the SWIFT environment, within secure zones, user endpoints, and supporting infrastructure.
These devices can bypass segmentation assumptions and introduce hidden risks that traditional controls may not detect.
2. Infrastructure Trust and Integrity Gaps
Unauthorized network devices or unmanaged switches can create unintended connectivity paths and expose SWIFT systems to external access.
Without hardware-level validation, organizations cannot fully trust how systems are connected or whether infrastructure changes introduce risk.
3. Gaps in Asset Integrity
Security controls rely on the assumption that systems, endpoints, and supporting infrastructure are known and secure.
However, without continuous validation of hardware identity and asset inventory, spoofed devices, or hidden components can undermine these controls.
Delivering Device Truth for SWIFT CSCF v2026 Compliance
Sepio supports SWIFT Customer Security Controls Framework requirements by delivering hardware-level visibility, independent device identity validation, and continuous detection of unauthorized devices across your SWIFT environment.
By extending security beyond software and network controls, Sepio ensures that every device within SWIFT secure zones is identified, verified, and continuously monitored, strengthening trust, reducing blind spots, and improving detection of hidden threats.

Comprehensive Asset Inventory
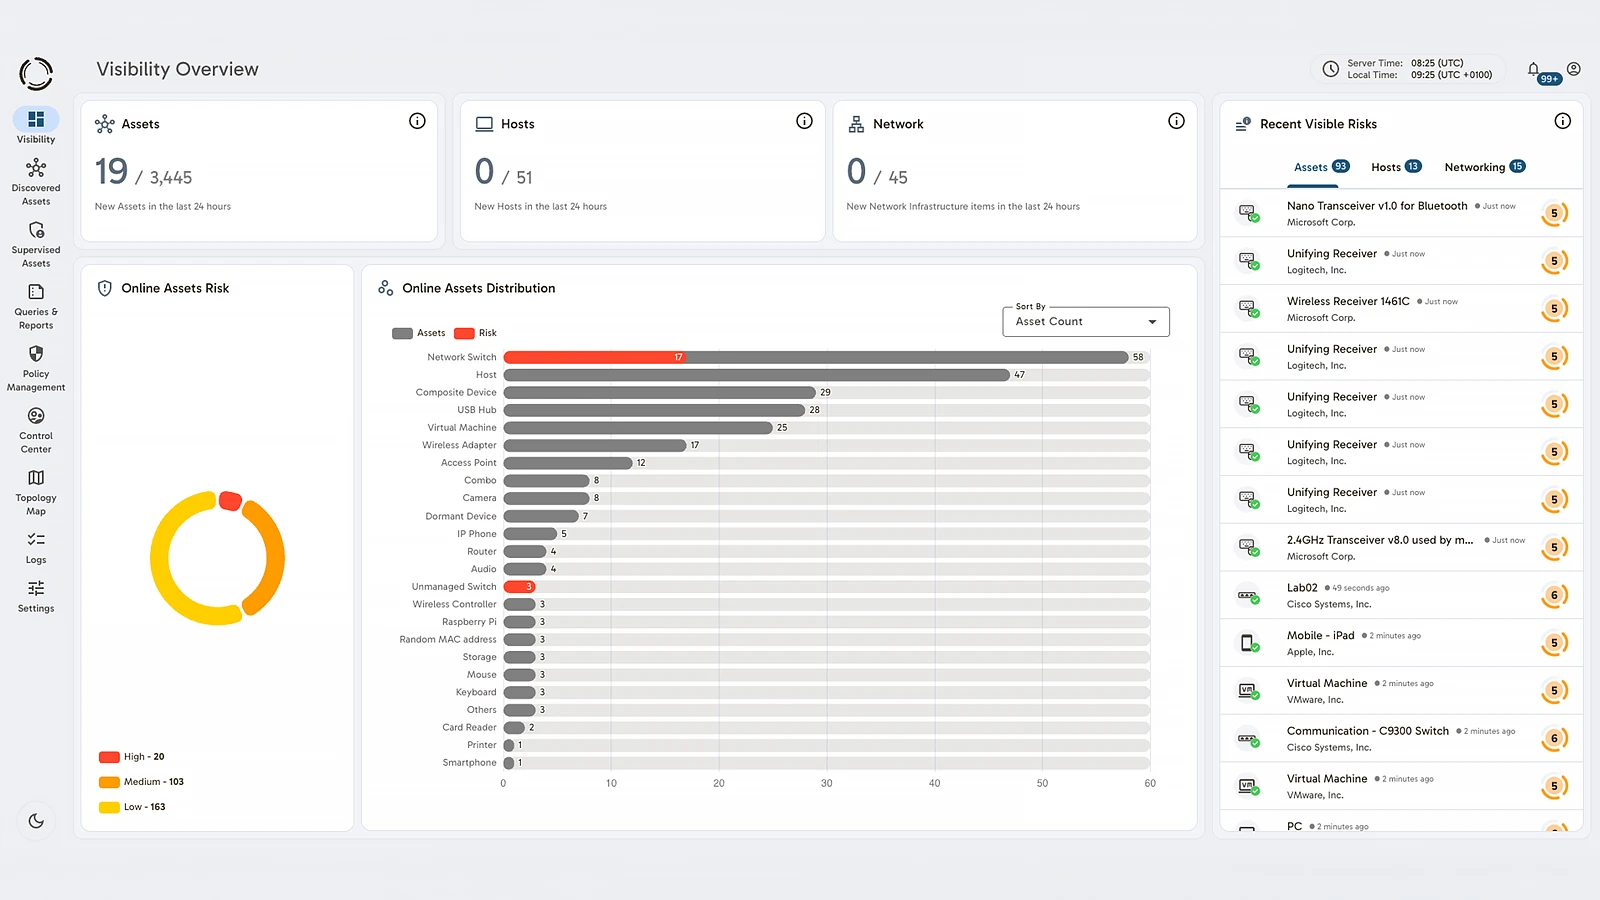
Achieve complete visibility into all devices connected to your SWIFT environment, across networks, endpoints, and infrastructure.
Maintain an updated inventory of what assets exist, where they are, and how they are connected.

Independent Device Validation
Validate each device using its intrinsic hardware characteristics, independent of software or network identifiers.
Ensure every device is genuine, authorized, and resistant to spoofing or impersonation.

Rogue Device Detection
Continuously identify unmanaged, unauthorized, or suspicious devices operating within SWIFT secure zones.
Detect hidden threats early and respond before they impact security or compliance.

Continuous Monitoring and Control
Monitor device behavior, movement, and policy compliance in real time across your SWIFT environment.
Maintain continuous assurance with actionable visibility and control over all connected hardware assets.
Compliance Positioning by Control Cluster

Secure The Environment
Sepio acts as a continuous hardware validation layer for secure zones, ensuring that only trusted and authorized devices are present.

Reduce Attack Surface
Sepio improves SWIFT infrastructure security by identifying unmanaged, misclassified, or suspicious devices that increase exposure.

Physically Secure The Environment
Sepio enhances physical security by validating device identity and providing location context, strengthening traditional facility controls.

Know And Limit Access
Sepio complements IAM, PAM, and MFA by enforcing device trust in SWIFT secure zones, ensuring access originates from trusted hardware.

Detect And Respond
Sepio delivers hardware-level monitoring for SWIFT security, enriching SIEM/SOAR workflows and enabling faster threat detection.

Incident Response And Risk Exercises
Sepio enables realistic SWIFT hardware security scenarios, including rogue devices, USB threats, and supply-chain attacks.
Evidence Package Sepio Can Provide
Sepio supports SWIFT compliance requirements with:
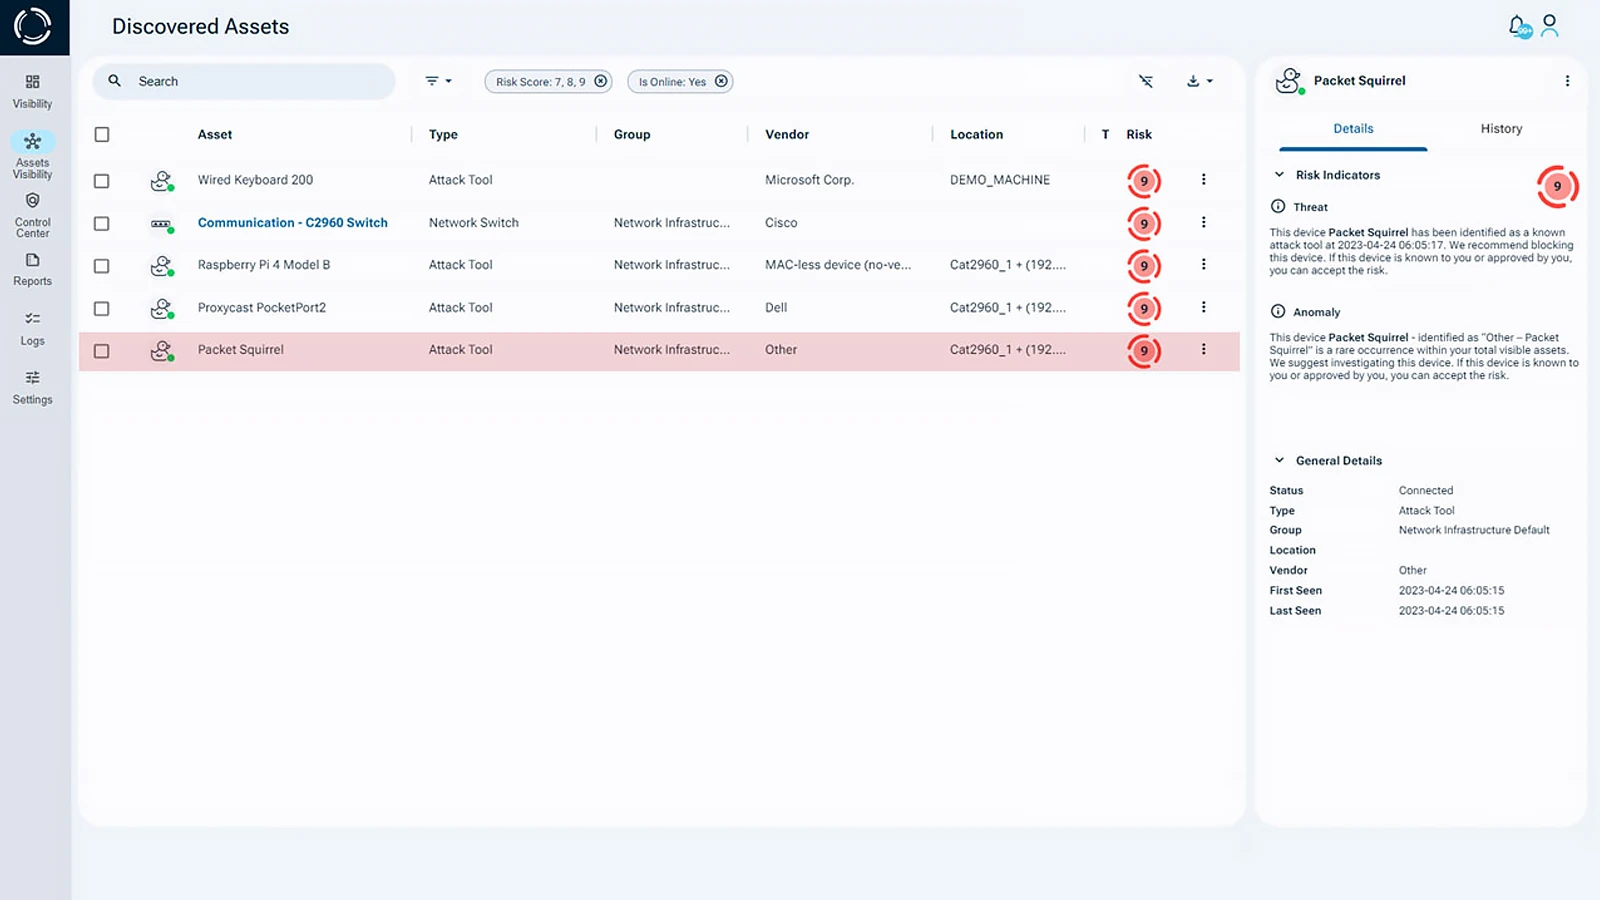
- Comprehensive asset inventory for SWIFT environments
- Validated device identity and trust classification
- Asset history (first seen, last seen, movement and policy violation events)
- Rogue, unknown, spoofed, or non-compliant device alerts
- Physical location context (switch, port, endpoint, USB)
- Integration logs or event forwarding evidence to SIEM, SOAR, CMDB, NAC, ticketing, or case-management systems.
- Incident response and forensic reporting
- Policy enforcement for trusted vs unauthorized hardware
Important Boundaries and Non-Claims
To ensure accurate positioning, the following clarifies what Sepio does, and does not, provide within the context of SWIFT CSCF compliance:- Not a SWIFT attestation solution: Sepio does not certify or attest SWIFT CSCF compliance and should not be positioned as a standalone certification or audit tool.
- Does not replace core security controls: Sepio does not replace segmentation, firewall policy, encryption, MFA, password policy, PAM, IAM, transaction controls, database integrity controls, or formal incident response governance.
- Complements existing controls: Sepio enhances the security stack by adding a hardware trust, visibility, detection, and forensic evidence layer, helping reduce device-related blind spots.
- Environment-dependent applicability: The relevance and implementation of controls depend on each organization’s SWIFT architecture, in-scope systems, and operational environment.
Customer-Facing Compliance Value
Physical Security Support: Validates identity, location, and status of devices in SWIFT environments.
Logging And Monitoring: Provides hardware-level telemetry and event data for SIEM/SOAR.
Intrusion Detection: Detects rogue and spoofed devices without relying on traffic inspection.
Vulnerability Scanning Support: Enhances asset visibility and risk context for hidden or misclassified devices.
Scenario-Based Risk Assessment: Supports planning for hardware-based attack scenarios.
Evidence And Investigation Value: Delivers investigation-ready visibility, history, and device context.
Extending SWIFT Security to the Hardware Layer
Sepio enhances SWIFT CSCF v2026 compliance by providing deep visibility into physical assets supporting SWIFT operations. It enables accurate inventories, detects rogue devices, and strengthens monitoring within SWIFT secure environments.
By focusing on hardware-level security for SWIFT, Sepio closes a critical gap left by traditional controls that focus only on users, applications, and network activity.
Strengthen SWIFT Compliance with Trusted Device Visibility
Sepio gives you full confidence in the devices supporting your SWIFT environment through continuous device visibility and trusted hardware validation.
Reduce risk, improve compliance readiness, and strengthen your SWIFT cybersecurity posture with complete hardware awareness.
Request a demo to see how Sepio supports SWIFT CSCF v2026 compliance and secure your SWIFT environment.